IndexLane Redirect & Internal Link Auditor
A WordPress plugin for finding broken internal links, redirects and old URLs left behind after a migration. It shows you where those links are used and takes you to the place where you can edit them.
 DownloadVersion 0.7.0
Images
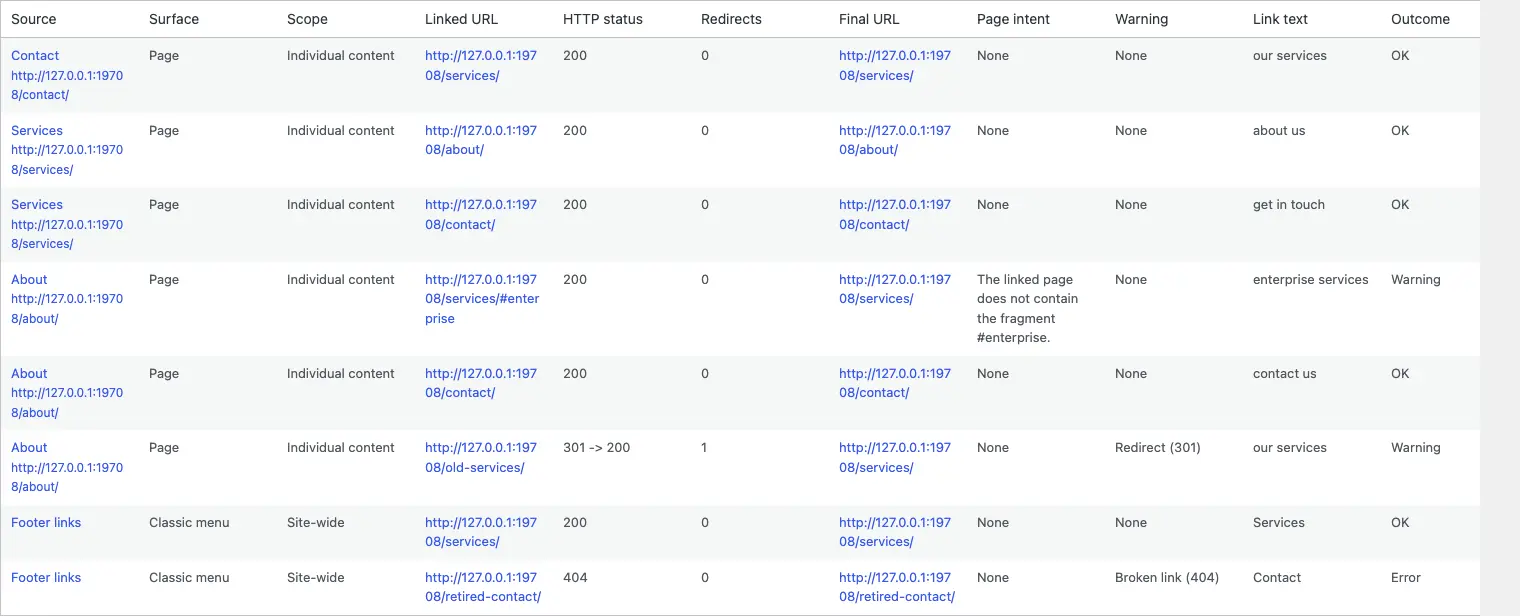
About IndexLane Redirect & Internal Link Auditor
Finding a broken URL is usually only half the job. Then you have to work out where the thing actually lives. A page? An old menu? A reusable block? That footer template you haven’t opened in six months?
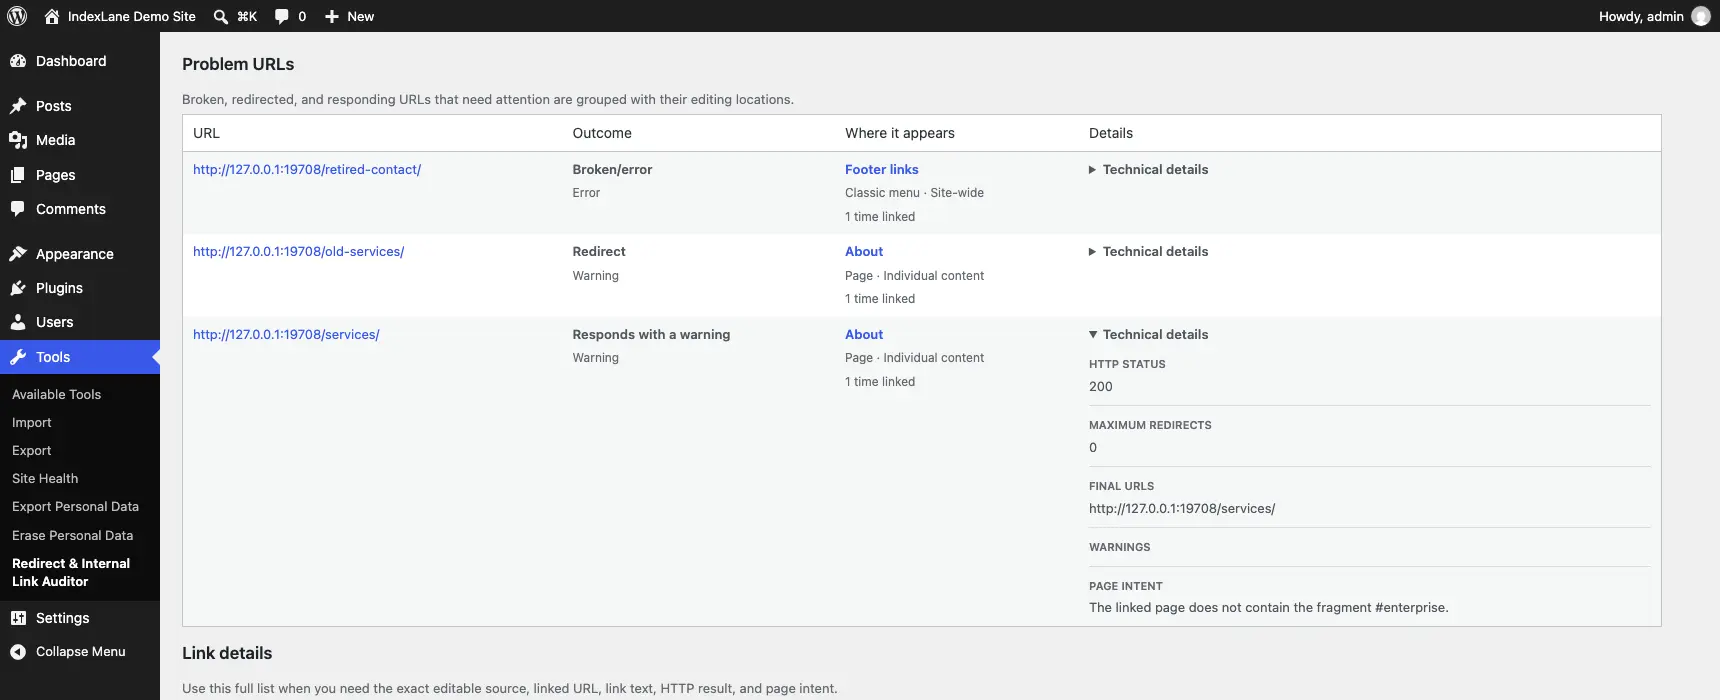
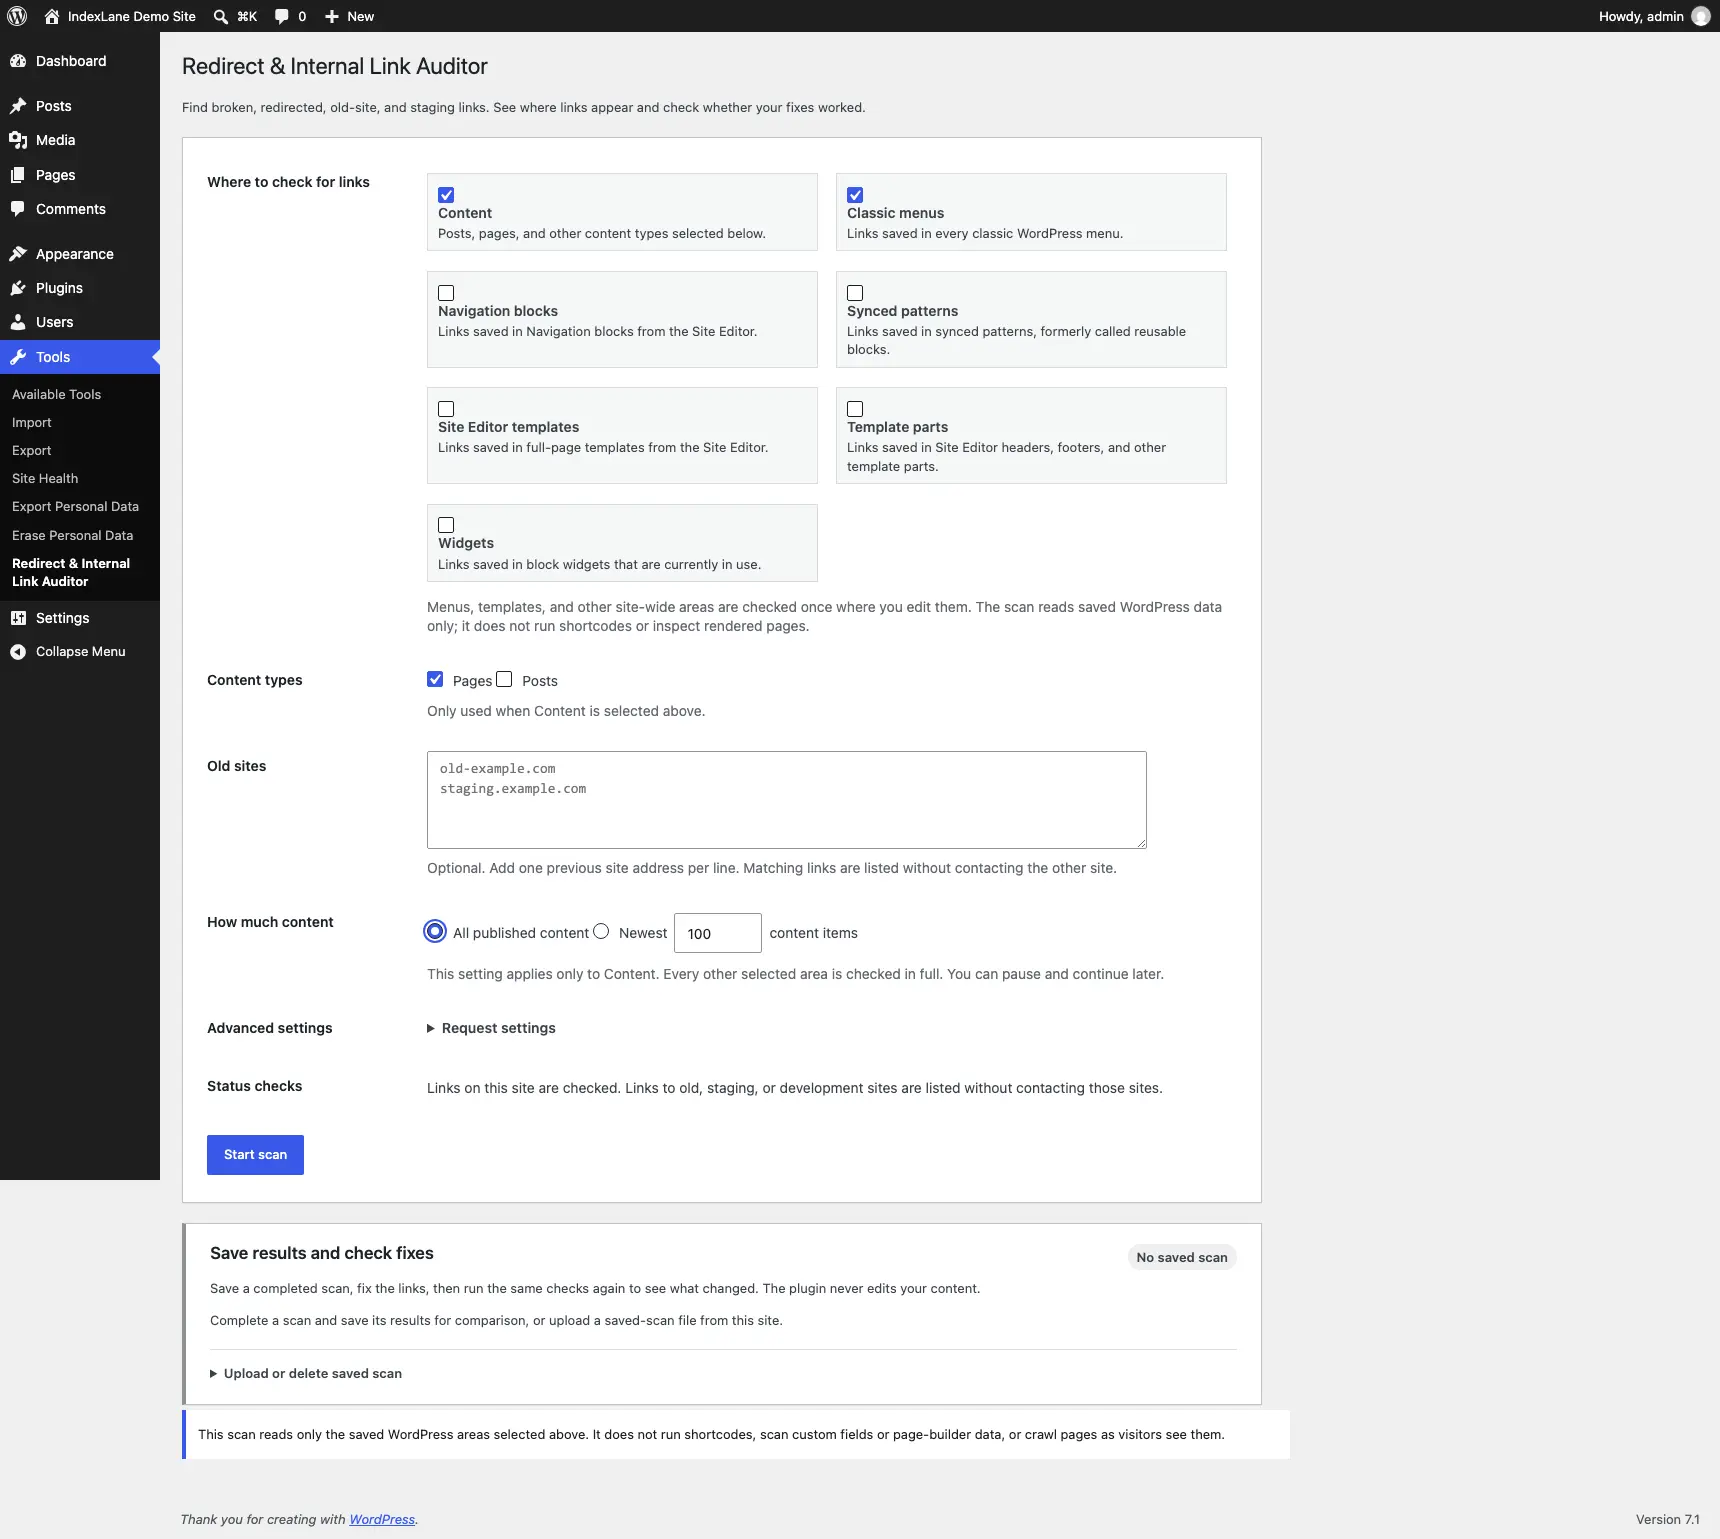
Redirect & Internal Link Auditor connects the problem to its source. You choose which areas to check, and the report shows the affected pages, menus, patterns and supported block templates, with links to their editors. Shared links are traced back to the place where they’re maintained, so you can fix a footer link in the footer.
It checks broken destinations, redirect chains and loops, and links pointing to old or staging domains. It can also flag links whose destination loads but still needs a closer look: a page marked noindex, a canonical pointing elsewhere, or a link to a section that no longer exists.
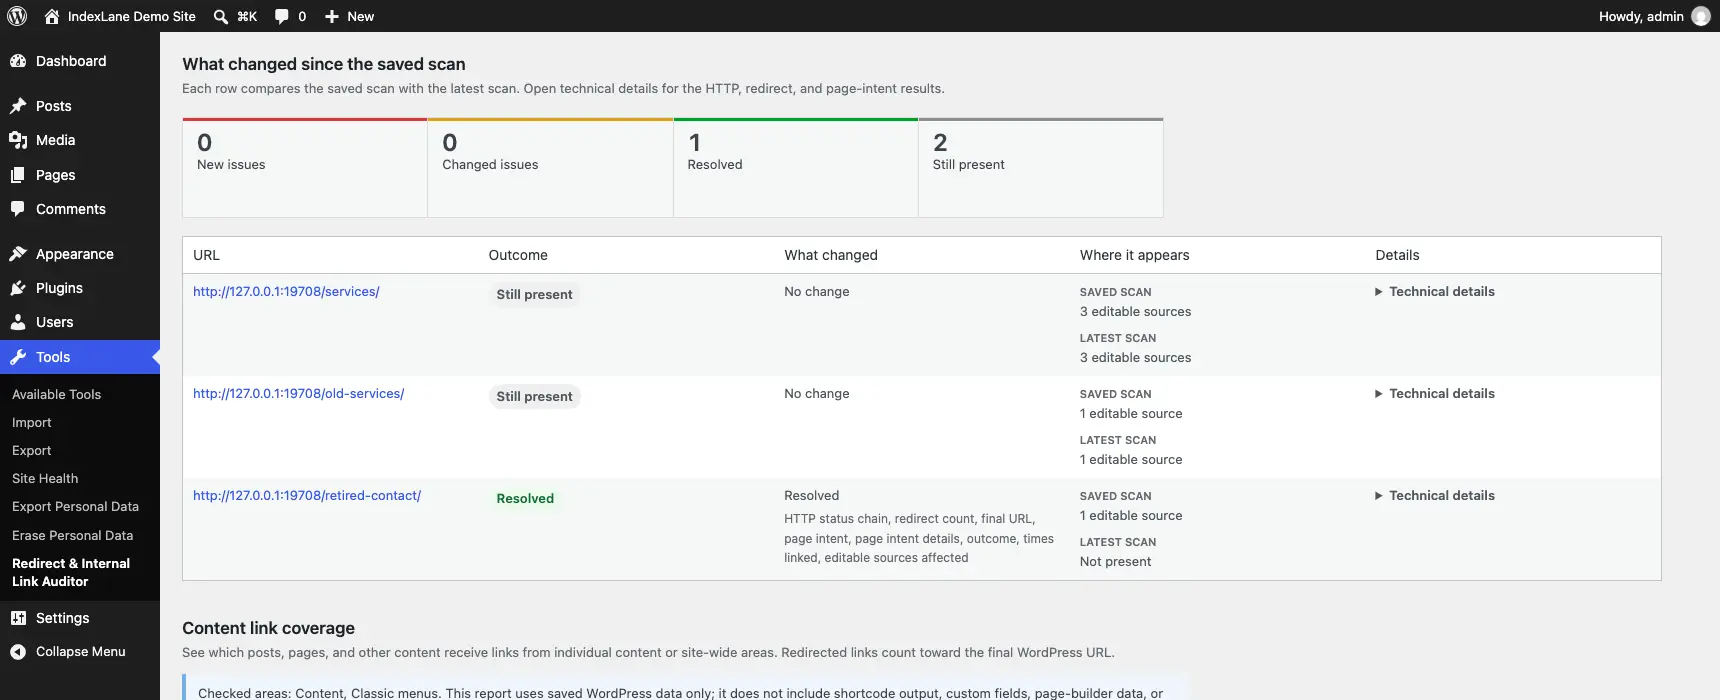
The saved-scan feature is particularly useful when you’re working through a cleanup. Save the results before making changes, fix the links in WordPress, then run the same checks again. The comparison shows what’s resolved, what’s still there, and whether anything new has appeared. You can export that to CSV if you need to keep a record or send the results to a client.
It checks stored WordPress content and supported areas of the site. Links generated by shortcodes or tucked away in unsupported page-builder data are outside its coverage.
It’s free, open source and runs when you ask it to. You make the edits; the plugin helps you find the problem and check the result.
Release history
Version 0.7.0
- Added destination-intent auditing for internal URLs that respond successfully but declare a different or off-site canonical, noindex, a meta refresh, or a missing linked fragment.
- Kept transport outcomes dominant and reported file responses, inconclusive fragments, and page/internal nofollow as informational evidence.
- Reused bounded final-response evidence across link occurrences without extra HTTP requests or retaining response bodies.
- Added page intent to Problem URLs, Link details, saved-scan comparisons, and CSV exports; retained strict import compatibility with 0.5 and 0.6 saved scans.
- Fixed literal HTML being mistaken for metadata, exact and numeric fragment matching, partial-response handling, relative canonical bases, Navigation-block rel evidence, and UTF-8 byte limits.
- Updated the WordPress.org listing, example CSVs, screenshots, walkthrough, release notes, and publishing commands.
External download
Download 0.7.0
Version 0.6.1
- Reworked the WordPress.org listing and README around migration checks, URL changes, and finding the exact editable source of a link.
- Added an illustrated scan, save, fix, and recheck walkthrough and direct links to the existing sample CSV reports.
- Replaced the public screenshots with a small demo showing a broken footer link, its editing location, and a genuine saved-scan comparison after editing the link.
- Corrected development-build wording and aligned plugin metadata, saved-scan version assertions, and release packaging for 0.6.1.
External download
Download 0.6.1
Version 0.6.0
- Added independently selectable link-source adapters for normal content, classic menus, Navigation entities, synced patterns, block templates, template parts, and assigned block widgets.
- Retained each occurrence's stable source identity, source surface, edit and source URLs, link text, and individual-content or site-wide scope alongside the existing HTTP and redirect evidence.
- Expanded content coverage, problem-URL reports, details, comparisons, and CSV exports with contextual and site-wide counts plus exact editable locations.
- Added the public
indexlane_rila_source_providersfilter for bounded third-party stored-source adapters without executing shortcodes, scanning arbitrary metadata, or crawling rendered pages. - Upgraded resumable session and portable saved-scan schemas with strict legacy migration, provider availability checks, five-source batches, and a 100,000-source session limit.
- Reworked the scan form and result wording for non-technical administrators, regenerated the WordPress.org screenshots, and expanded behavioral, integration, translation, and authenticated AJAX coverage.
External download
Download 0.6.0
Version 0.5.1
- Rewrote the administrator workflow around saved scans, fix checks, results, URLs, link details, and downloads without changing the plugin name or read-only behavior.
- Put the first scan form before the empty saved-scan panel and current scan progress before saved-scan details.
- Moved request controls into collapsed advanced settings and moved request accounting, exact settings, schema data, and raw JSON downloads into technical details.
- Reduced comparison, content-coverage, and problem-URL tables to their primary decisions while retaining HTTP, redirect, final-URL, and before/after data in expandable details.
- Simplified completed-scan summaries, added correct singular/plural labels, grouped downloads by purpose, and updated CSV headings.
- Regenerated all WordPress screenshots and expanded behavioral, integration, translation, and authenticated AJAX coverage for the revised interface.
External download
Download 0.5.1
Version 0.5.0
- Added one opt-in, site-specific baseline per administrator with strict JSON export, import, replacement, and deletion controls.
- Added exact-scope verification scans bound to the saved baseline revision so fixes can be compared without silently changing scope.
- Added new, changed, resolved, and still-present issue classifications with explicit before-and-after evidence and a comparison CSV export.
- Split the plugin implementation into focused admin, scan, report, and baseline modules while preserving the existing runtime class and public behavior.
- Updated packaging, documentation, screenshots, translation auditing, behavioral tests, WordPress integration tests, and authenticated AJAX coverage for the complete baseline lifecycle.
External download
Download 0.5.0
Version 0.4.0
- Added destination-oriented content link coverage for every published content item in a completed scan.
- Added incoming and outgoing link counts, distinct linking sources and destinations, anchor-text variants, self-link counts, and direct-versus-redirected evidence.
- Added a target detail view and a filter for content with zero or one detected linking source.
- Resolved redirected links to their final published WordPress content item while retaining the original redirect evidence and making no additional HTTP requests.
- Added an exact-session target-coverage CSV export, updated screenshots and documentation, and expanded behavioral, integration, translation, and authenticated AJAX coverage.
External download
Download 0.4.0
Version 0.3.1
- Removed the authenticated AJAX end-to-end harness's undeclared ripgrep dependency so release validation runs on standard GitHub-hosted runners.
External download
Download 0.3.1
Version 0.3.0
- Replaced the bounded synchronous form request with authenticated, browser-driven WordPress AJAX batches.
- Added resumable per-administrator scan sessions for all published content or a numeric newest-content limit.
- Added selection for every registered public post type.
- Added live progress for content processed, links extracted, unique destinations checked, HTTP requests, and actionable issues.
- Added pause, continue, cancel, reload recovery, and explicit 250-request allowance extensions.
- Limited each AJAX batch to five content items and five actual outbound HTTP requests while allowing redirect chains to continue safely across batches.
- Deduplicated destination requests across the complete session without collapsing occurrence-level evidence.
- Limited CSV export to exact completed-session evidence and extended temporary per-user session retention to 24 hours of inactivity.
- Added automatic abandoned-session expiry without cron jobs, custom tables, telemetry, or content changes.
- Made all plugin-owned administrator, JavaScript, result, warning, and CSV strings translation-ready with literal gettext calls, translator notes, and the WordPress.org slug text domain.
- Added repeatable source auditing and local POT extraction verification without bundling translations.
- Added WordPress-loaded integration tests and authenticated AJAX end-to-end coverage.
External download
Download 0.3.0
Version 0.2.2
Release 0.2.2 admin stylesheet compliance
External download
Download 0.2.2
Version 0.2.1
- Renamed the pre-approval plugin to IndexLane Redirect & Internal Link Auditor and aligned its slug, text domain, runtime identifiers, tests, and package layout.
- Prepared plugin metadata and packaging for the WordPress.org Plugin Directory.
- Removed the third-party
Update URIso WordPress.org can deliver plugin updates. - Declared compatibility testing through WordPress 7.1.
- Corrected the WordPress.org contributor metadata.
- Resolved Plugin Check findings for translation loading, nonce verification, translatable labels, and CSV output.
- Moved the project release history to this root changelog instead of duplicating it in the README.
External download
Download 0.2.1
Version 0.2.0
WPFixPath Redirect & Internal Link Auditor 0.2.0
- Added a destination-centric impact view for broken/error and redirected targets.
- Grouped normalized destinations by total link occurrences and distinct affected content
- items.
- Preserved HTTP status, redirect-count, effective-final-URL, warning, and result
- evidence.
- Added deterministic severity, affected-source, occurrence, and URL ordering.
- Added a separate destination-impact CSV while preserving the detailed occurrence export.
- Derived both views from the exact saved scan without additional HTTP requests.
- Strengthened CSV formula-injection protection.
External download
Download 0.2.0
Version 0.1.3
Release 0.1.3 correctness fixes
External download
Download 0.1.3
Version 0.1.2
Refine README copy for 0.1.2
External download
Download 0.1.2
Version 0.1.1
Release 0.1.1 assets
External download
Download 0.1.1
Version 0.1.0
Initial commit
External download
Download 0.1.0
More software
IndexLane Safe WebP Queue
WordPress Version 1.0.1
A WordPress plugin that creates WebP copies of your images while keeping the originals. Convert on the server or use the optional browser mode when your host cannot write WebP, with progress reporting and checks before converted files are saved.
Classifieds & Advertising Platform — Go Rebuild
Go Version 1.17.10
An ongoing Go rebuild of my Laravel classifieds platform, with a React dashboard, incremental listing updates and background jobs handled through NATS JetStream. It preserves the existing platform’s behaviour while changing how the application processes and serves its data.
pgvector-filterbench
pgvector-filterbench
Go Version 0.1.2
A command-line tool for checking how pgvector search behaves once you add filters. It measures speed, compares approximate results with exact search, and checks query plans to see whether PostgreSQL is using your HNSW index.
wp-migrate-core
wp-migrate-core
Typescript Version 0.3.0
A command-line tool for getting a WordPress-to-Astro migration started. It reads a WordPress XML export, inventories content, images and links, and can generate an Astro project with a clear list of what still needs rebuilding.
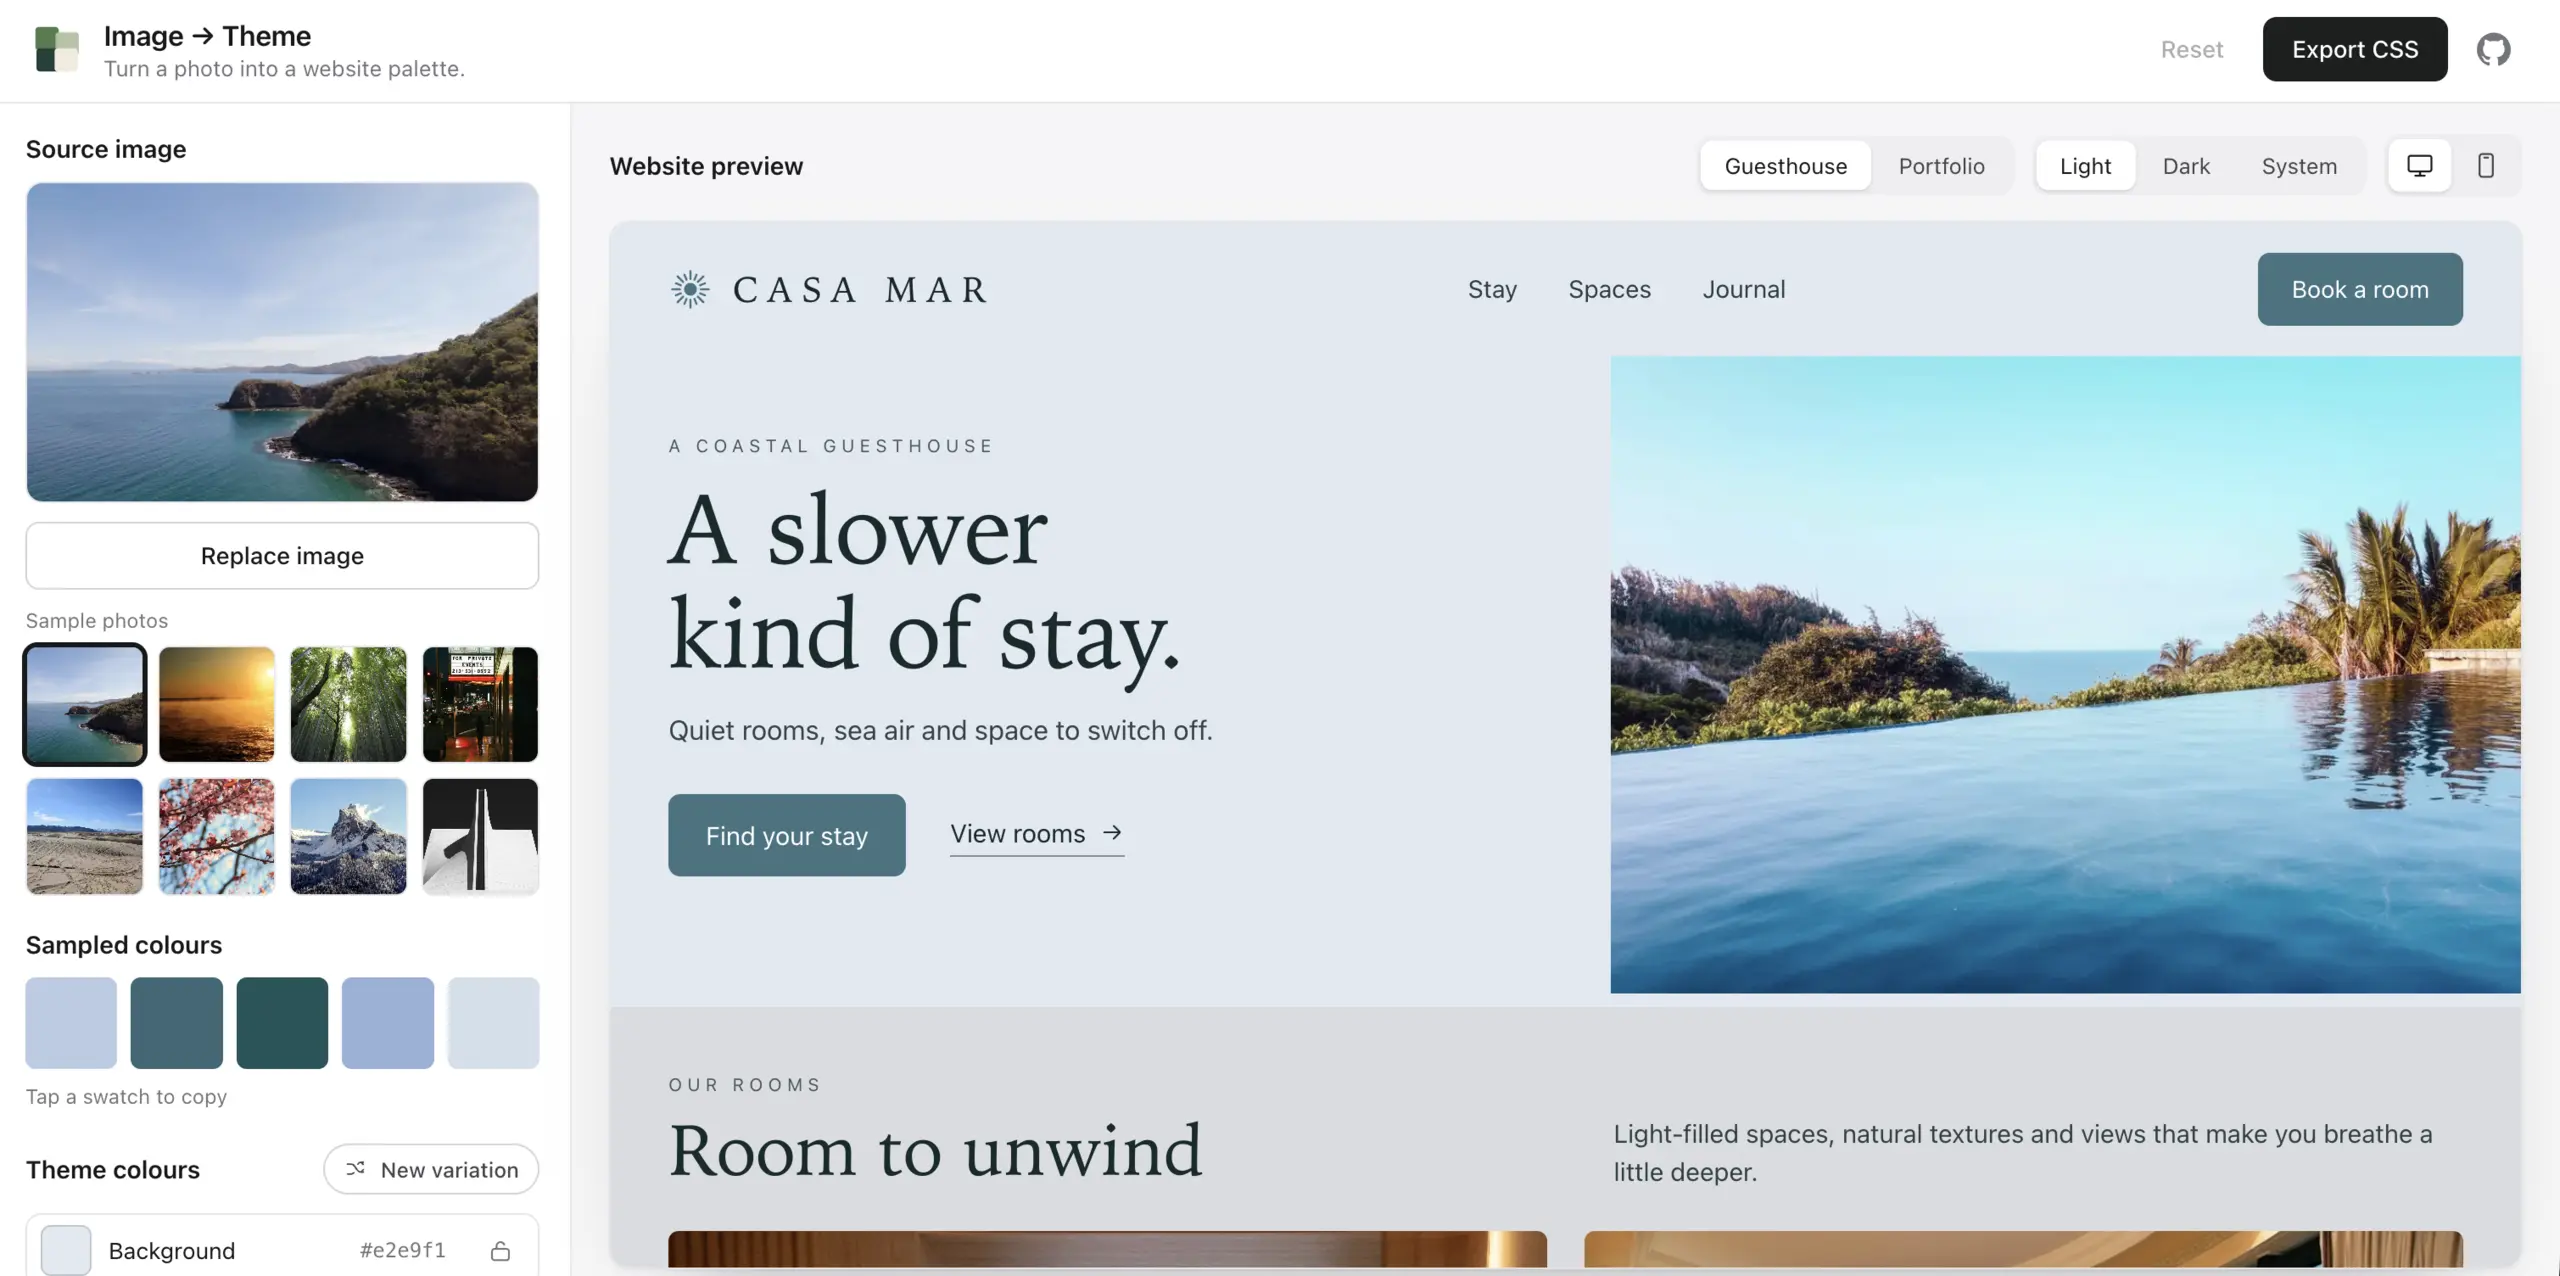
hueframe
TypeScript Version 1.0.3
A tool for turning a photo into a website color theme. Drop in an image, see its colors applied to a page, adjust the result and export it as CSS variables or JSON design tokens.
SSRWire
Typescript Version 0.5.0
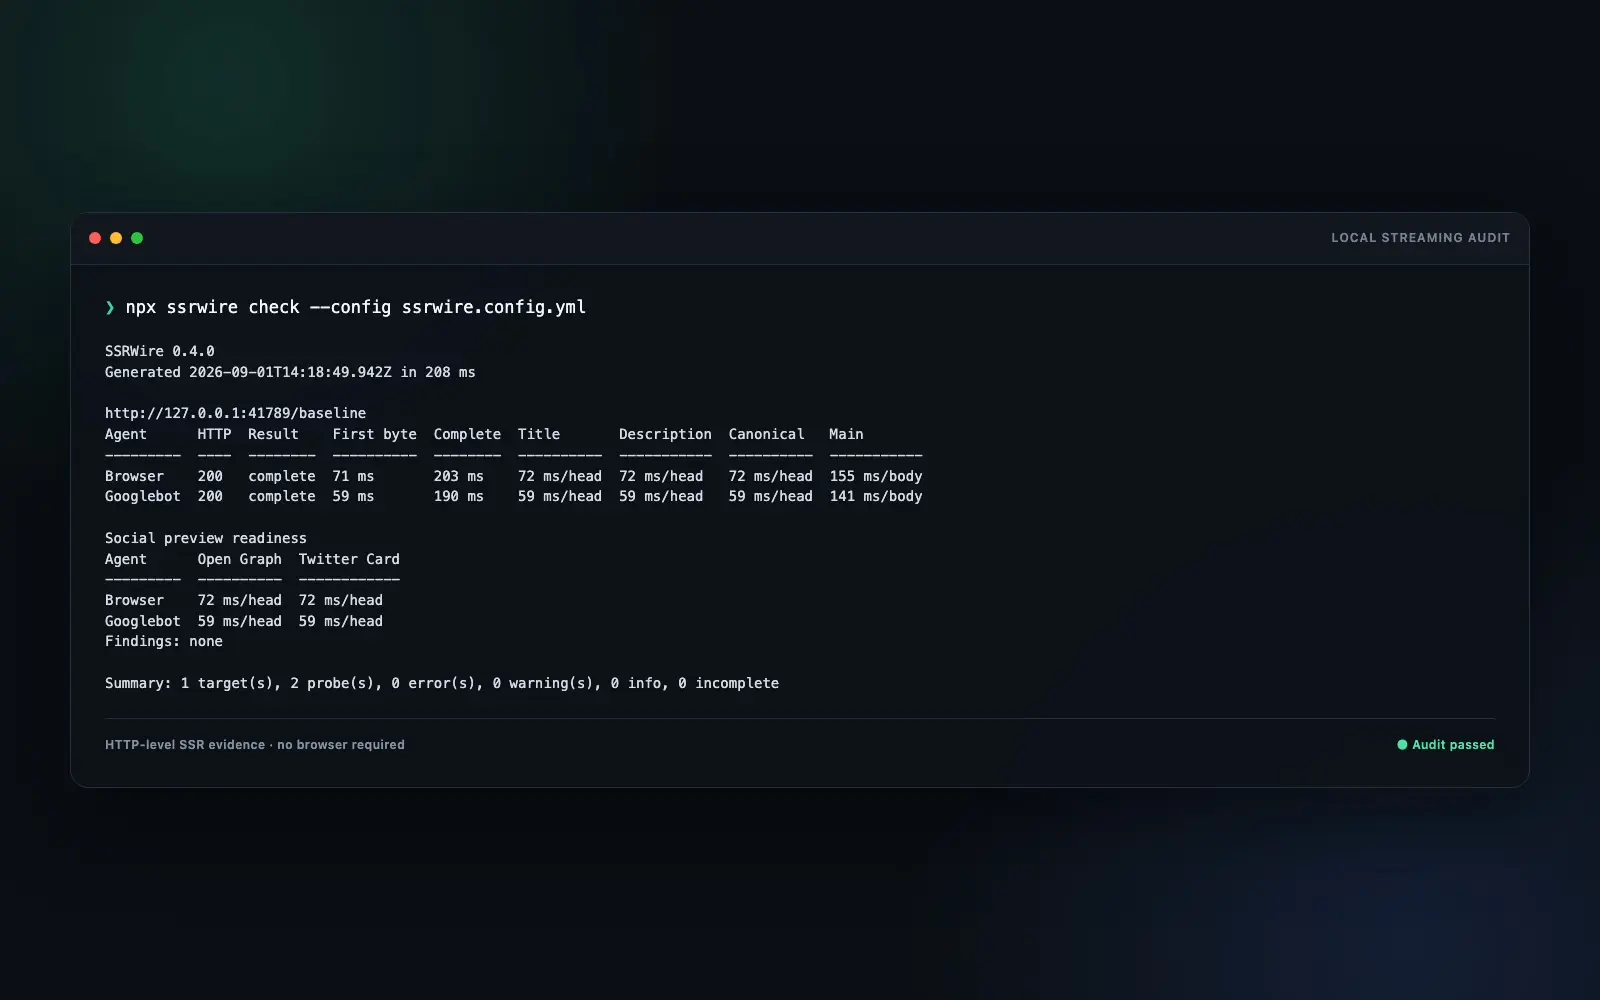
A command-line tool for inspecting the HTML your server sends, including content and metadata that arrive in a stream. It records when important elements appear and compares responses for different browser, search-crawler and social-preview user agents.
routeplay
routeplay
TypeScript Version 0.4.0
A command-line tool for checking that a page delivers the right content and metadata however you reach it. It compares the HTML your server sends, a fresh browser load and the result of clicking through from another page.
ReachLog
Typescript Version 0.2.1
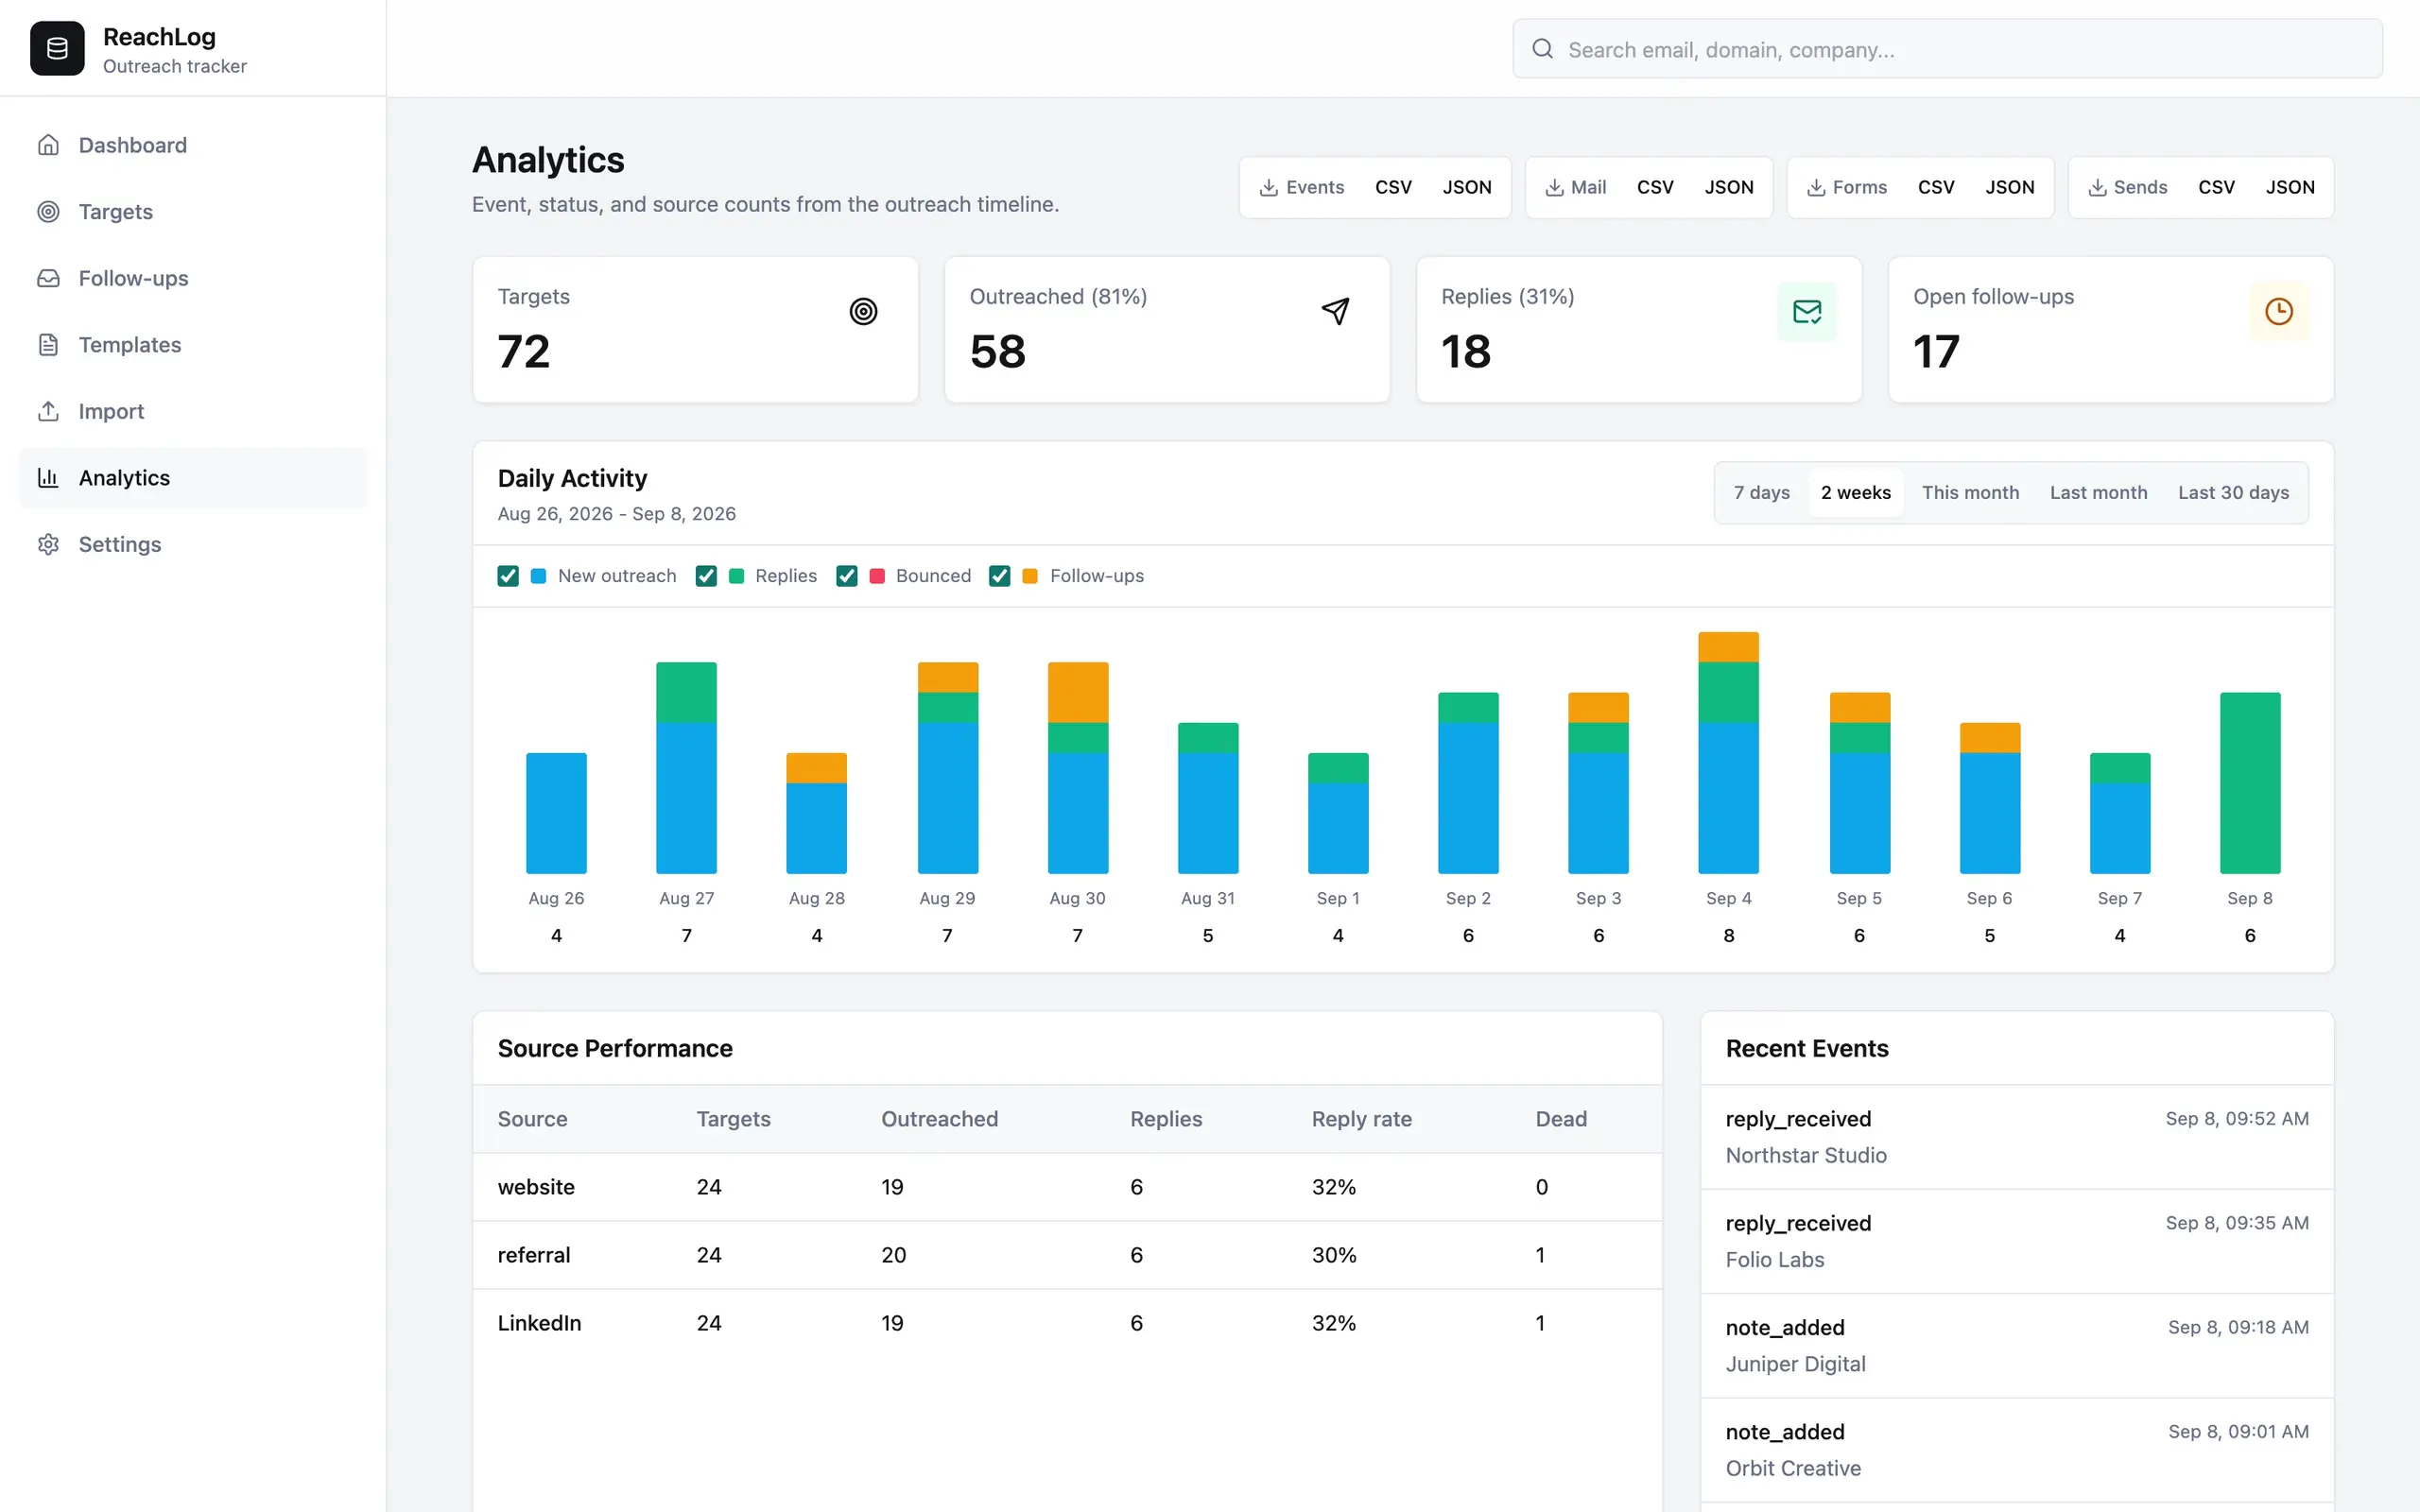
ReachLog is a small outreach and contact manager for keeping track of who you’ve contacted, what you’ve discussed and when to follow up. It brings contacts, companies and email conversations together in a local application that works with your existing email account.
routelint
routelint
TypeScript Version 0.3.1
A command-line tool for finding broken links, incorrect redirects and indexing conflicts on a live or preview website. It discovers URLs, checks what your server returns and gives you findings tied to specific pages, with the evidence behind them.
Data-Driven Publishing Platform
Data-Driven Publishing Platform
Laravel Version 0.14.1
A publishing platform for running several websites from structured source data. It handles imports, page generation, scheduled updates and search monitoring through one administration panel. Four domains are live; getting traffic to them remains the unfinished part.
Classifieds & Advertising Platform
Laravel Version 1.3.6
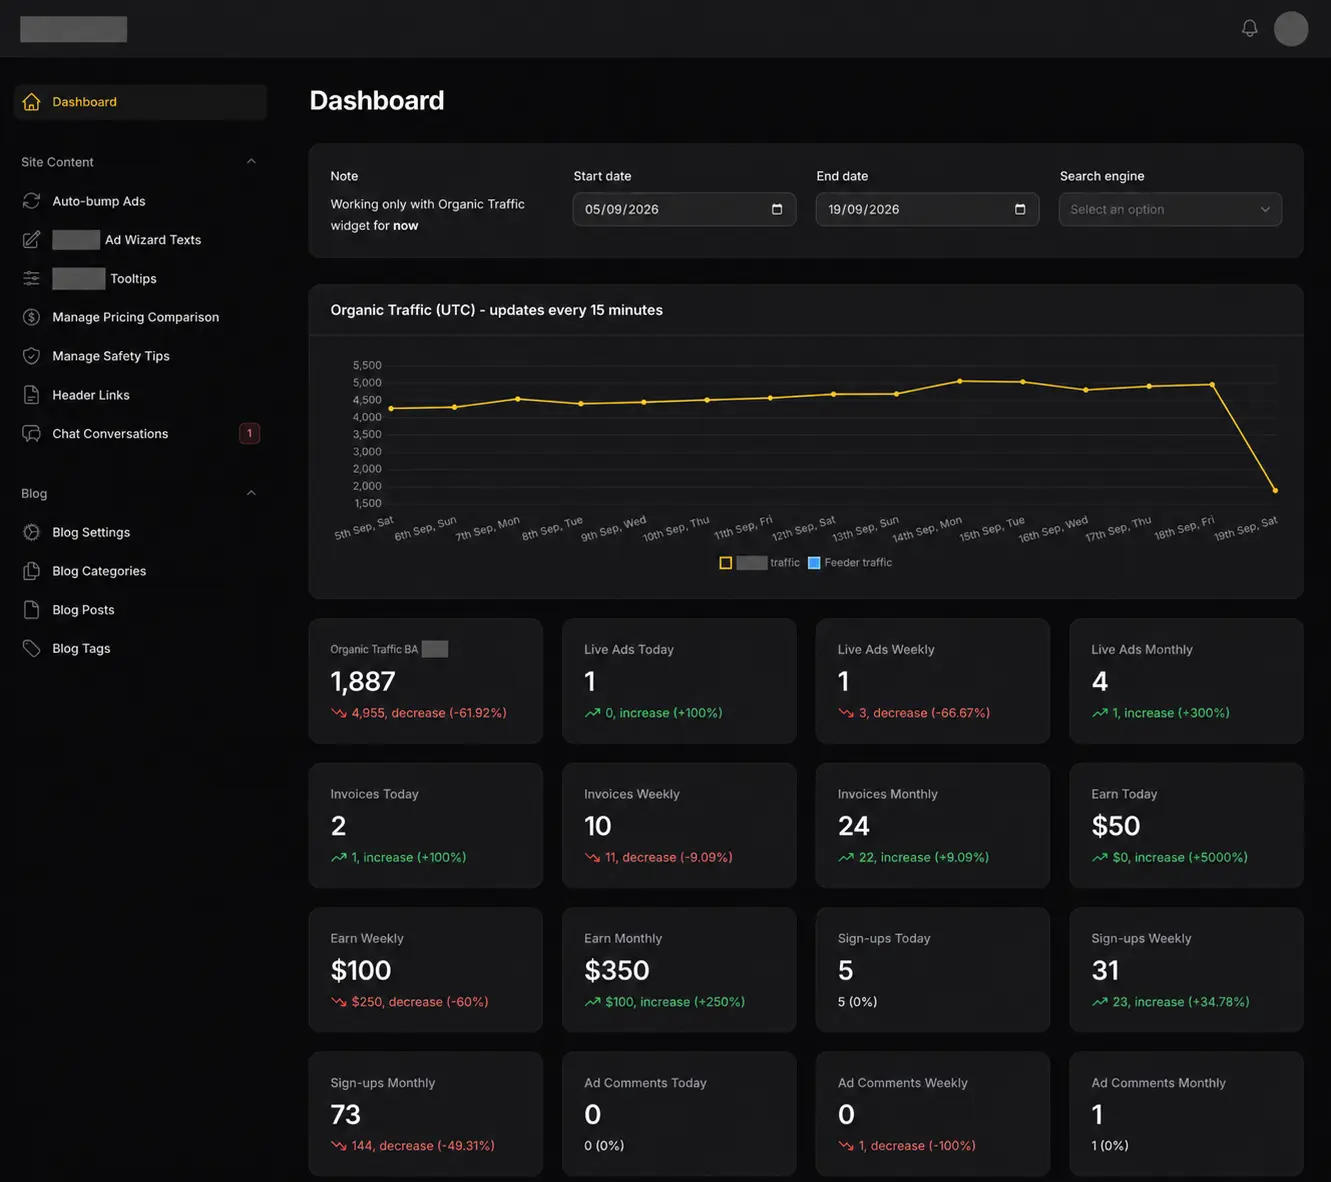
A classifieds and advertising platform I’ve been building and maintaining for roughly two years. It combines location-based browsing, advertiser dashboards, paid listings, invoicing, live chat and an administration panel for running the site.
Private Organic Search & LLM Activity Tracker
Elixir Version 0.39.19
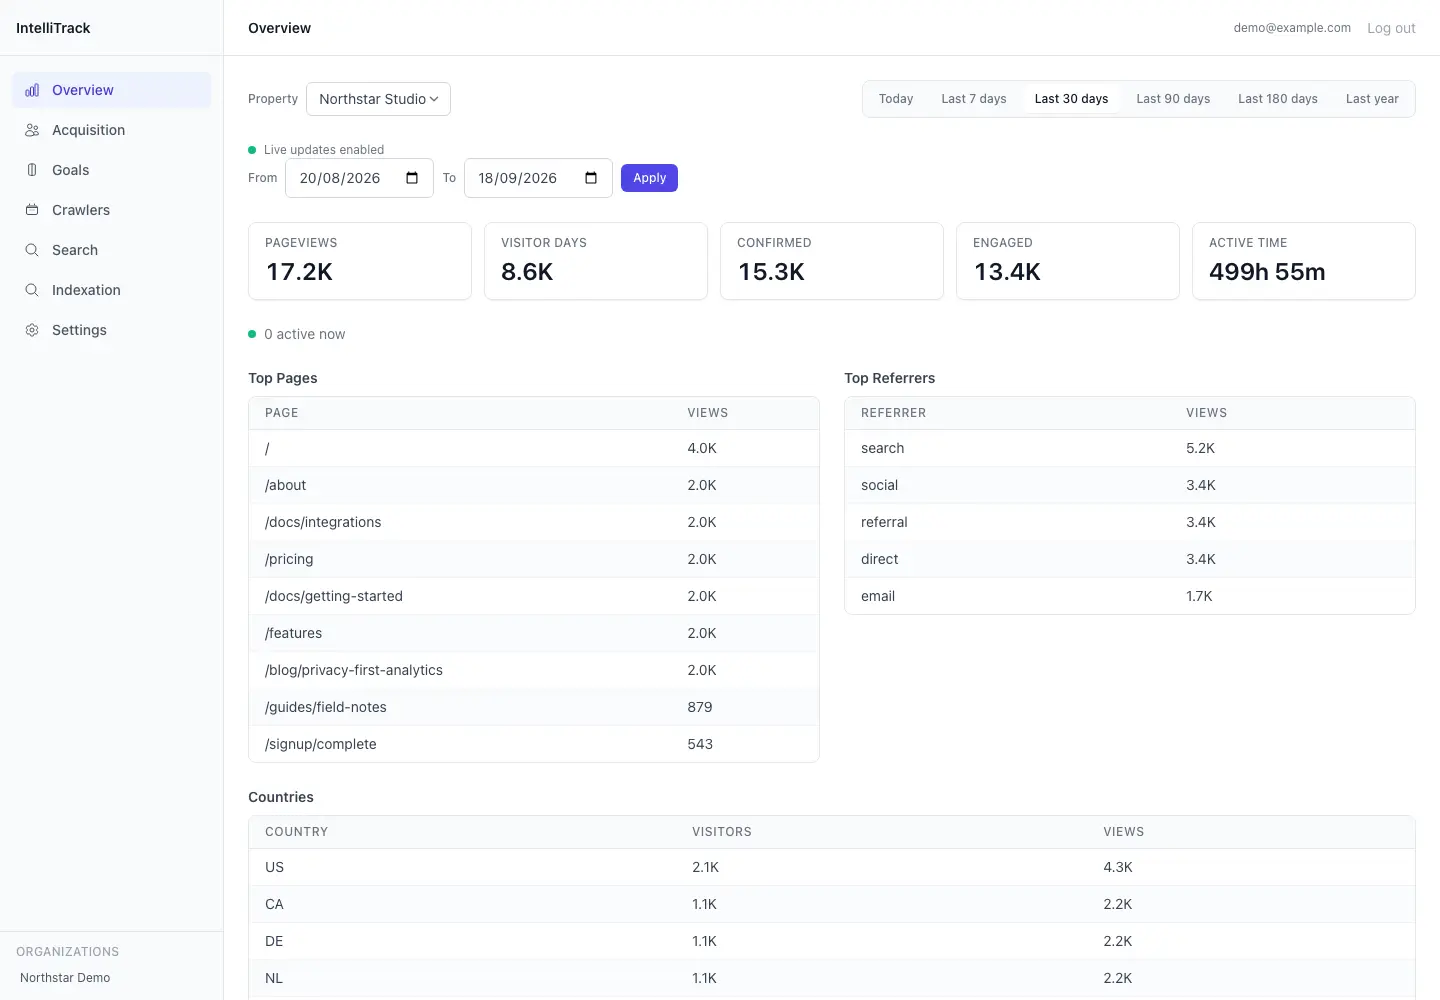
A private analytics tool for tracking website traffic, organic search performance, and activity from search engines and LLM crawlers. It brings ordinary visitor statistics, crawler requests, Google Search Console and Bing Webmaster Tools into one dashboard.
ILCrawler
Go Version 0.41.0
ILCrawler is the technical SEO crawler I use for my own websites and client audits. It brings page checks, links, screenshots, performance samples and reporting into one place. It’s also the project that repeatedly convinced me I was only one rewrite away from being happy with it.
crawlreplay
crawlreplay
Rust Version 0.1.0
A command-line tool for testing robots.txt changes and new deployments against URLs found in your server logs. It helps you catch newly blocked pages, broken responses and unexpected indexing changes before putting those changes live.
Data-Driven Publishing Platform — Go Rebuild
Data-Driven Publishing Platform — Go Rebuild
Go Version 0.226.2
An unlaunched Go rebuild of my publishing platform, using PostgreSQL for application data and background jobs, React for administration and Astro for public websites. It includes source processing, publishing checks and migration tools for the existing sites.
IndexLane Crawl Fetch Inspector
WordPress Version 0.2.0
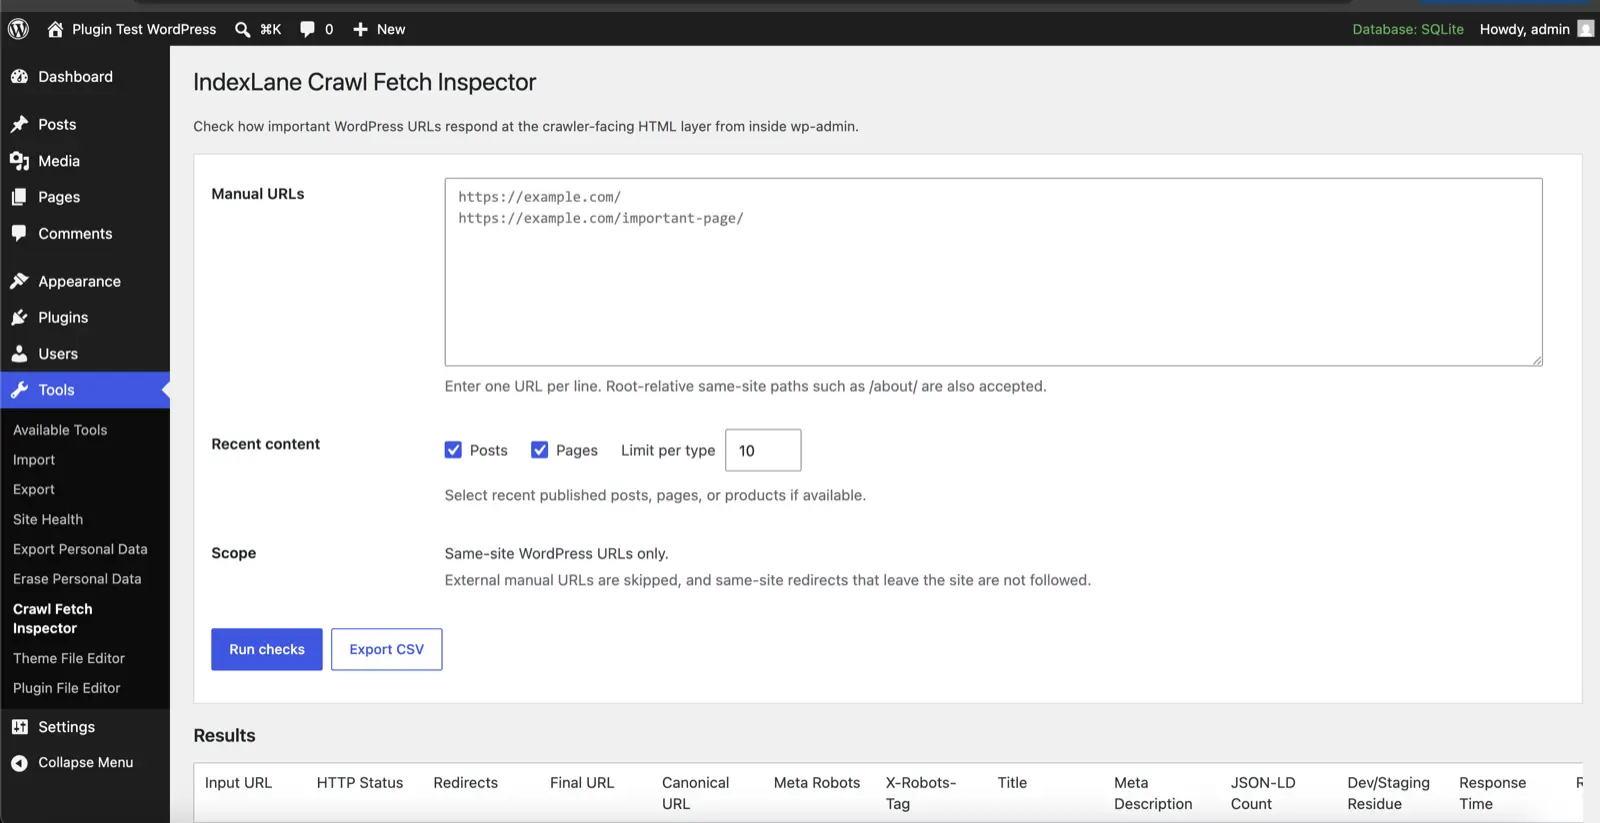
A WordPress plugin for checking redirects, indexing rules, sitemaps and structured data from your dashboard. Particularly handy when you’re launching a site or moving one.
IndexLane Asset Weight Snapshot
WordPress Version 0.2.0
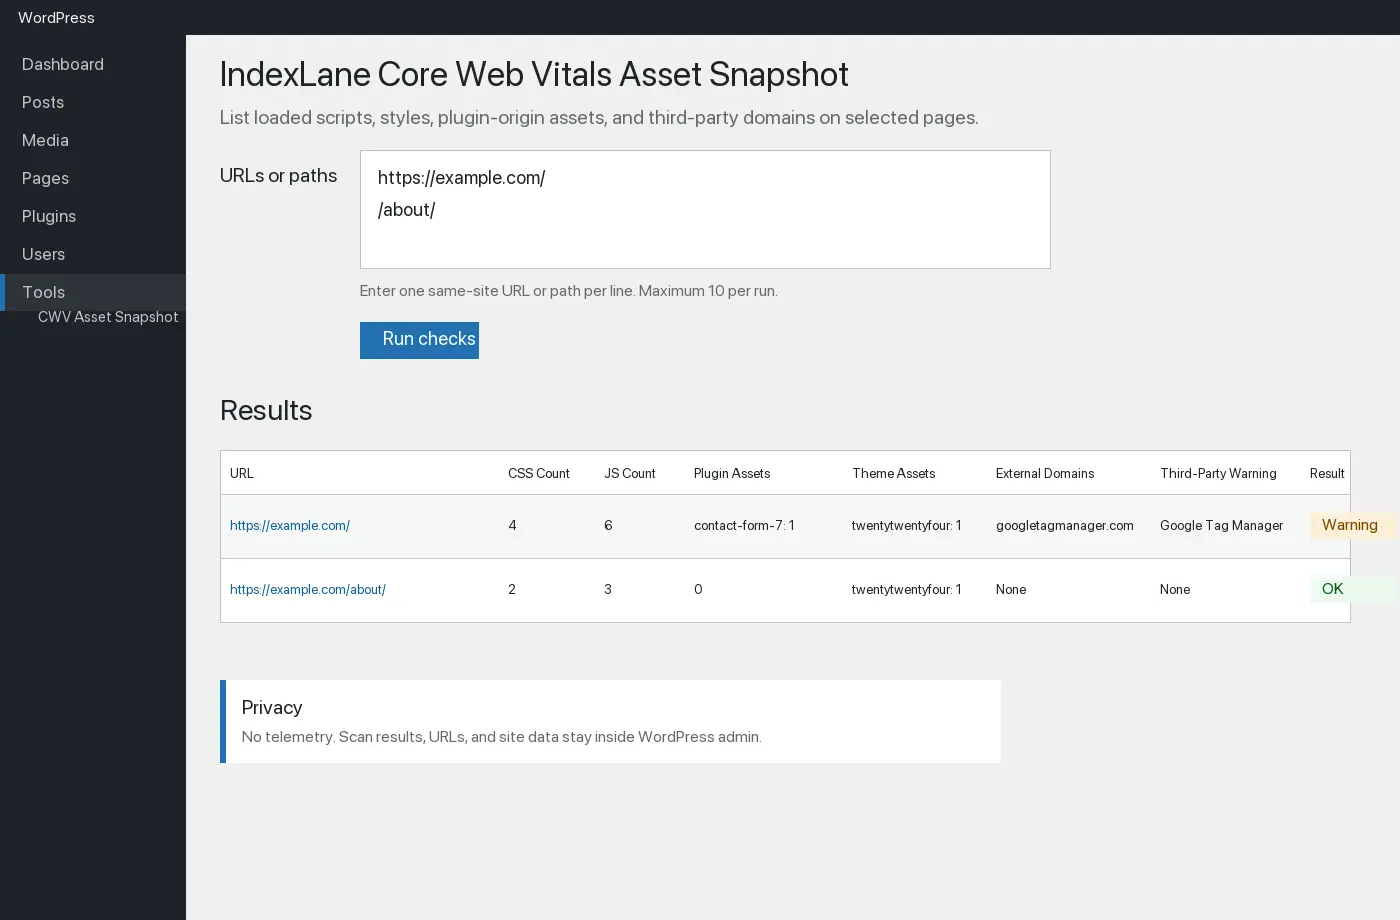
A WordPress plugin for checking the CSS and JavaScript your pages reference, measuring the files it can fetch, and comparing the results over time. Useful when you want to see what a plugin update or site change has added.
IndexLane Site Atlas
WordPress Version 0.1.0
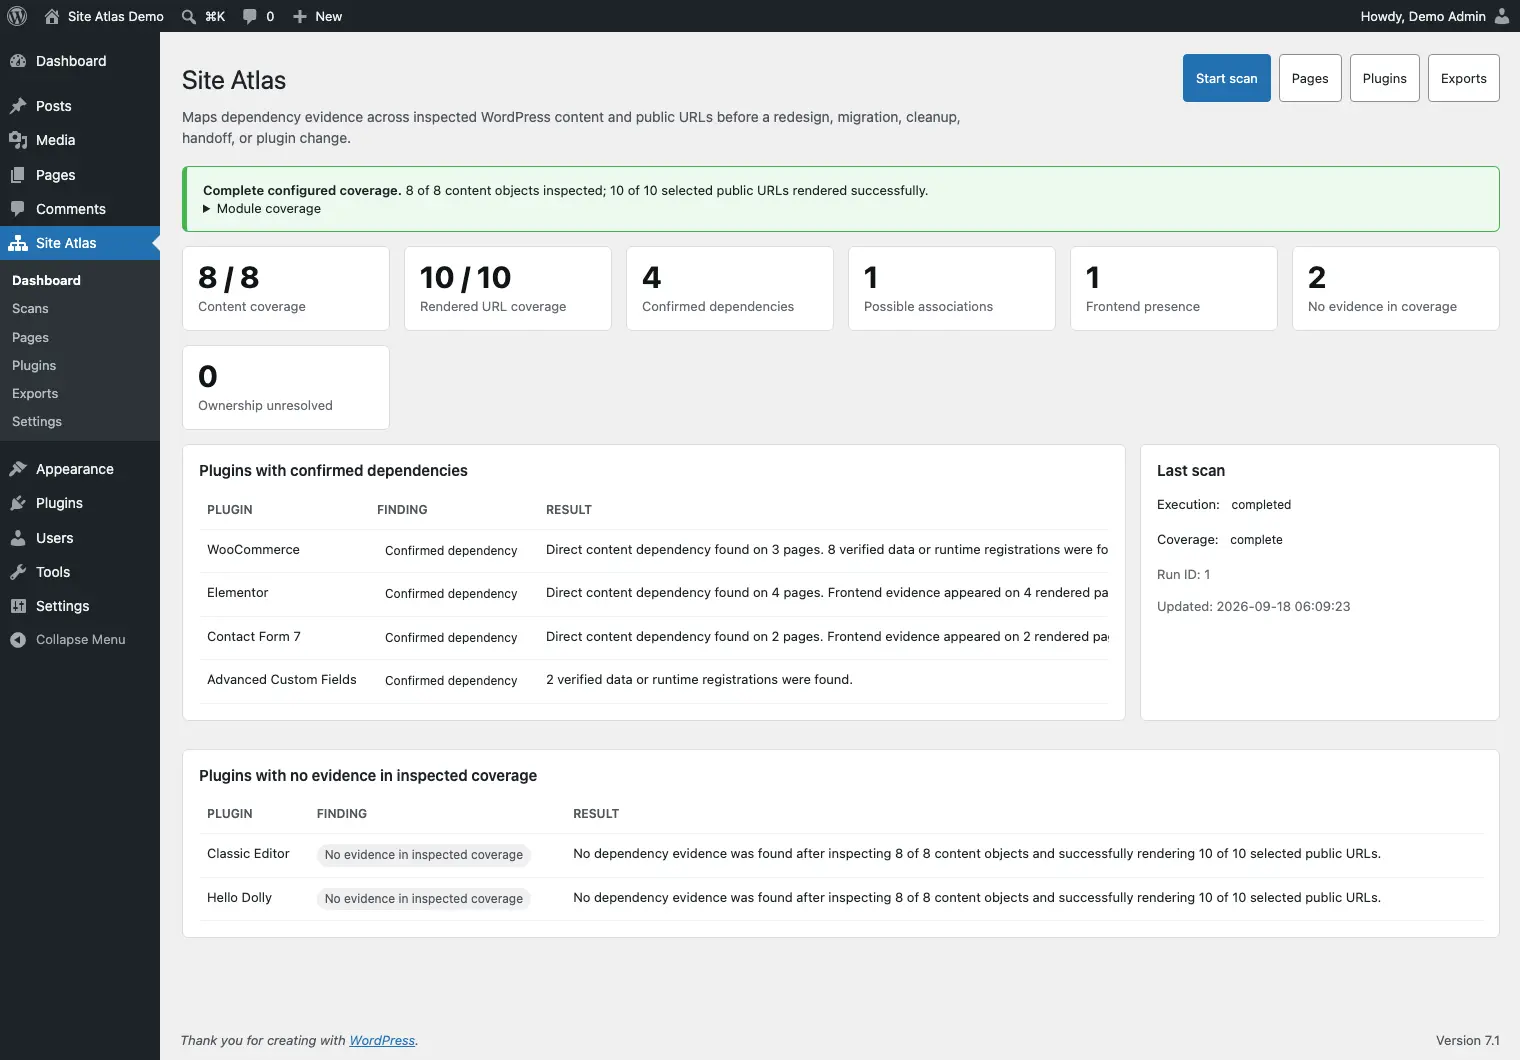
A WordPress plugin for figuring out how a site fits together before you start changing things. It looks at the connections between plugins, content and stored data, which is useful when you’re planning a cleanup, rebuild or handover.
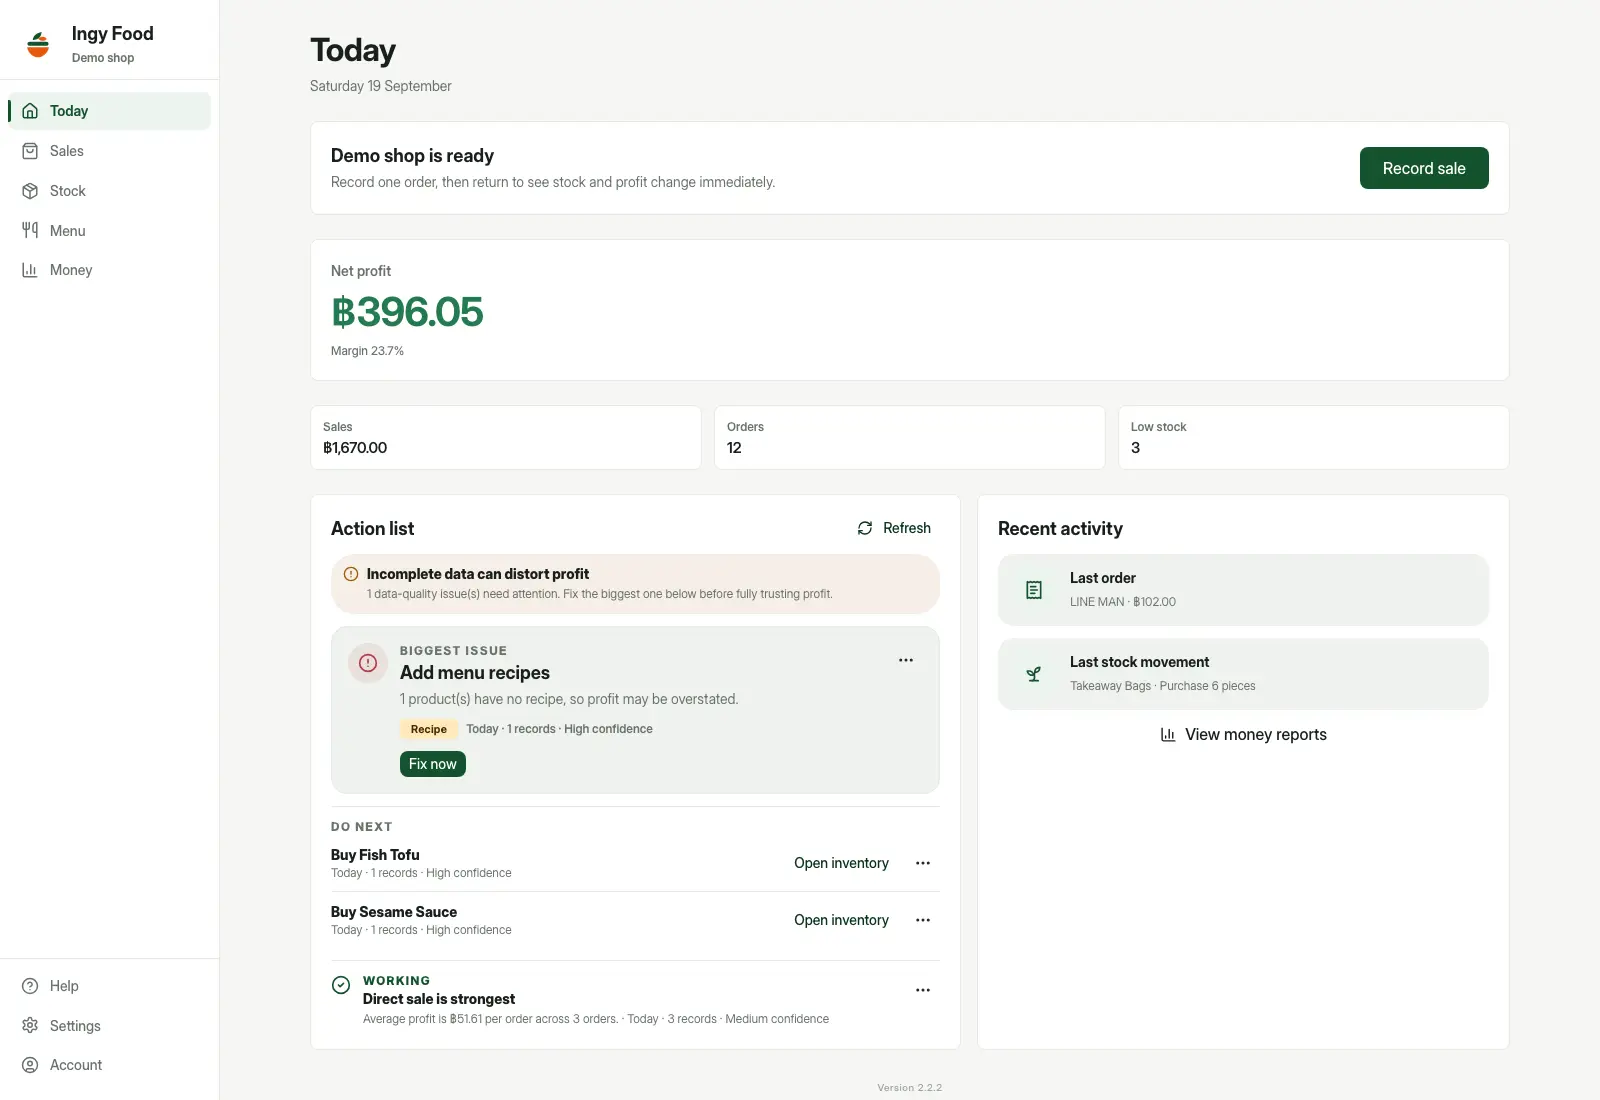
Food Cost & Profit Tracker
TypeScript Version 2.2.2
A private app for tracking food costs, stock and estimated profit across direct sales and food delivery. It connects ingredient purchases, recipes, orders and platform fees, helping a seller understand what each dish costs and how much money is actually left.
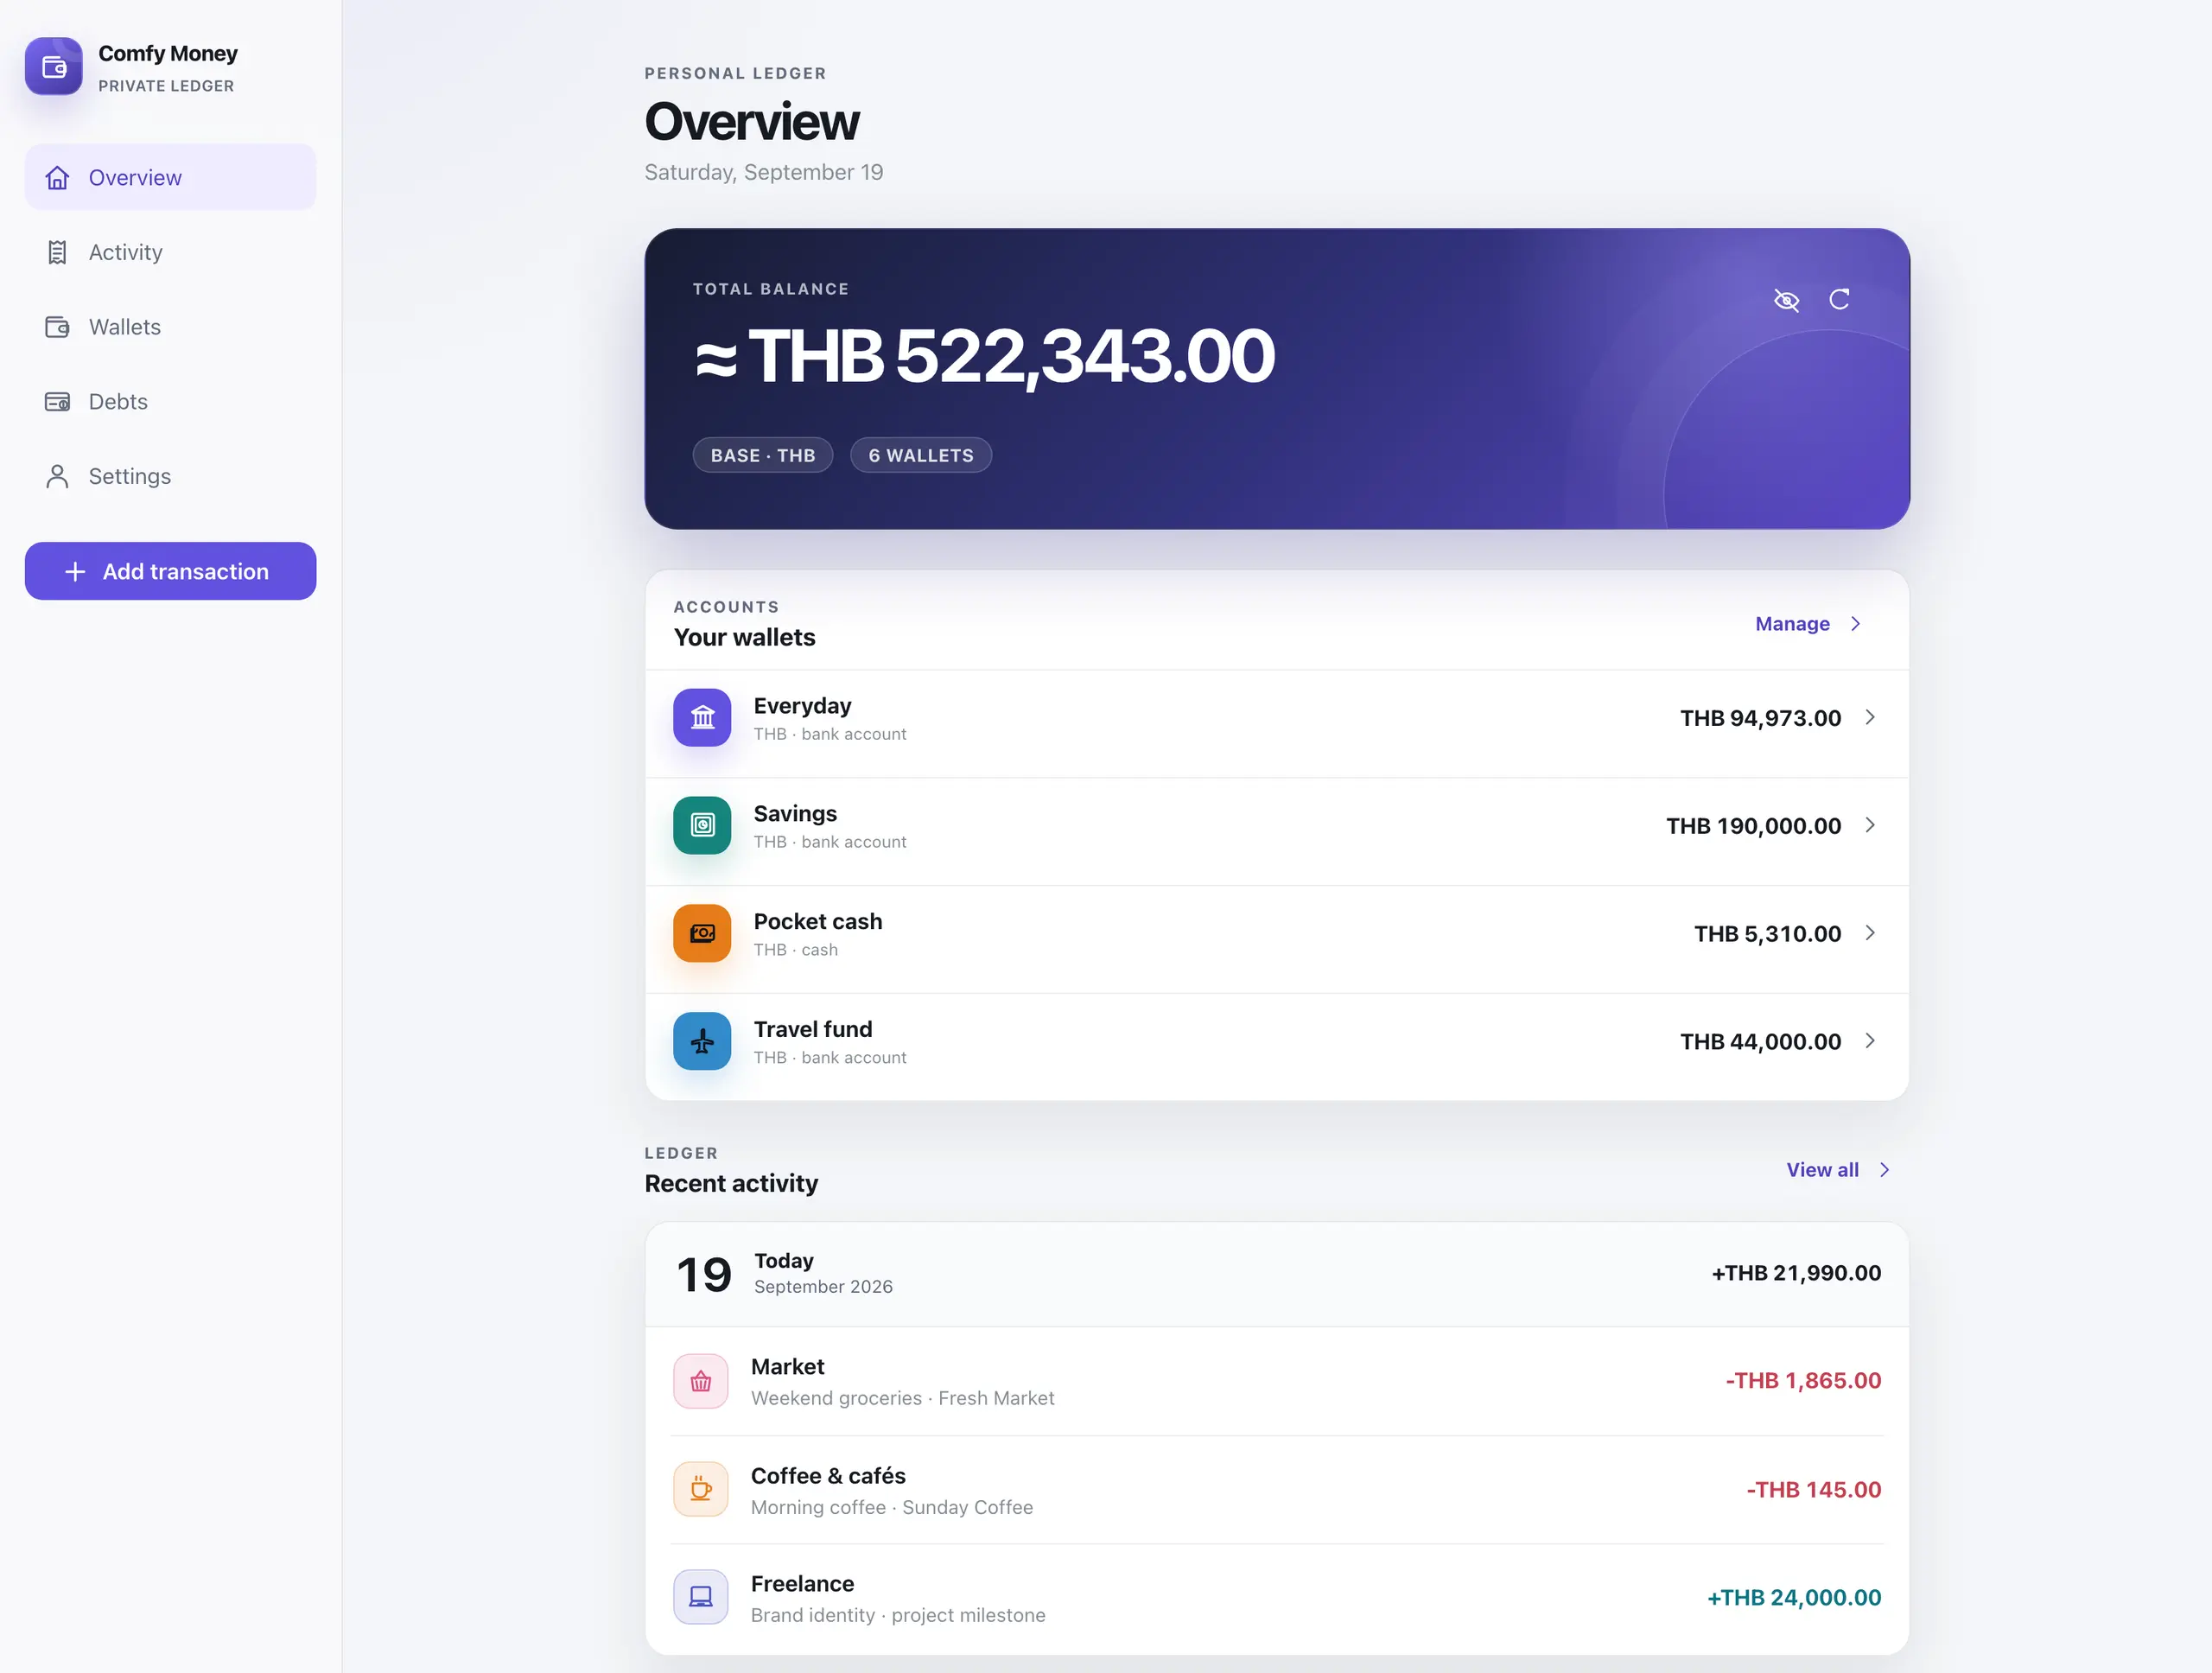
Comfy Money - Private Multi-Currency Ledger
Go Version 0.14.5
Comfy Money is a private money tracker I built for myself and my family. It handles wallets in different currencies, income, expenses, transfers, budgets and debts, with automatically updated exchange rates and a mobile interface that installs as a PWA.
crawlcontract
crawlcontract
Rust Version 0.3.1
A command-line tool for catching crawl and indexing problems when a website changes. It checks built files or pages fetched from a live or preview site, and compares scans so you can spot problems before a release.
pgvector-index-manager
pgvector-index-manager
Go Version 0.1.1
A command-line tool for keeping your pgvector indexes in line with a configuration you control. It checks what exists, shows you what needs changing, and can build and replace HNSW indexes when you apply those changes.
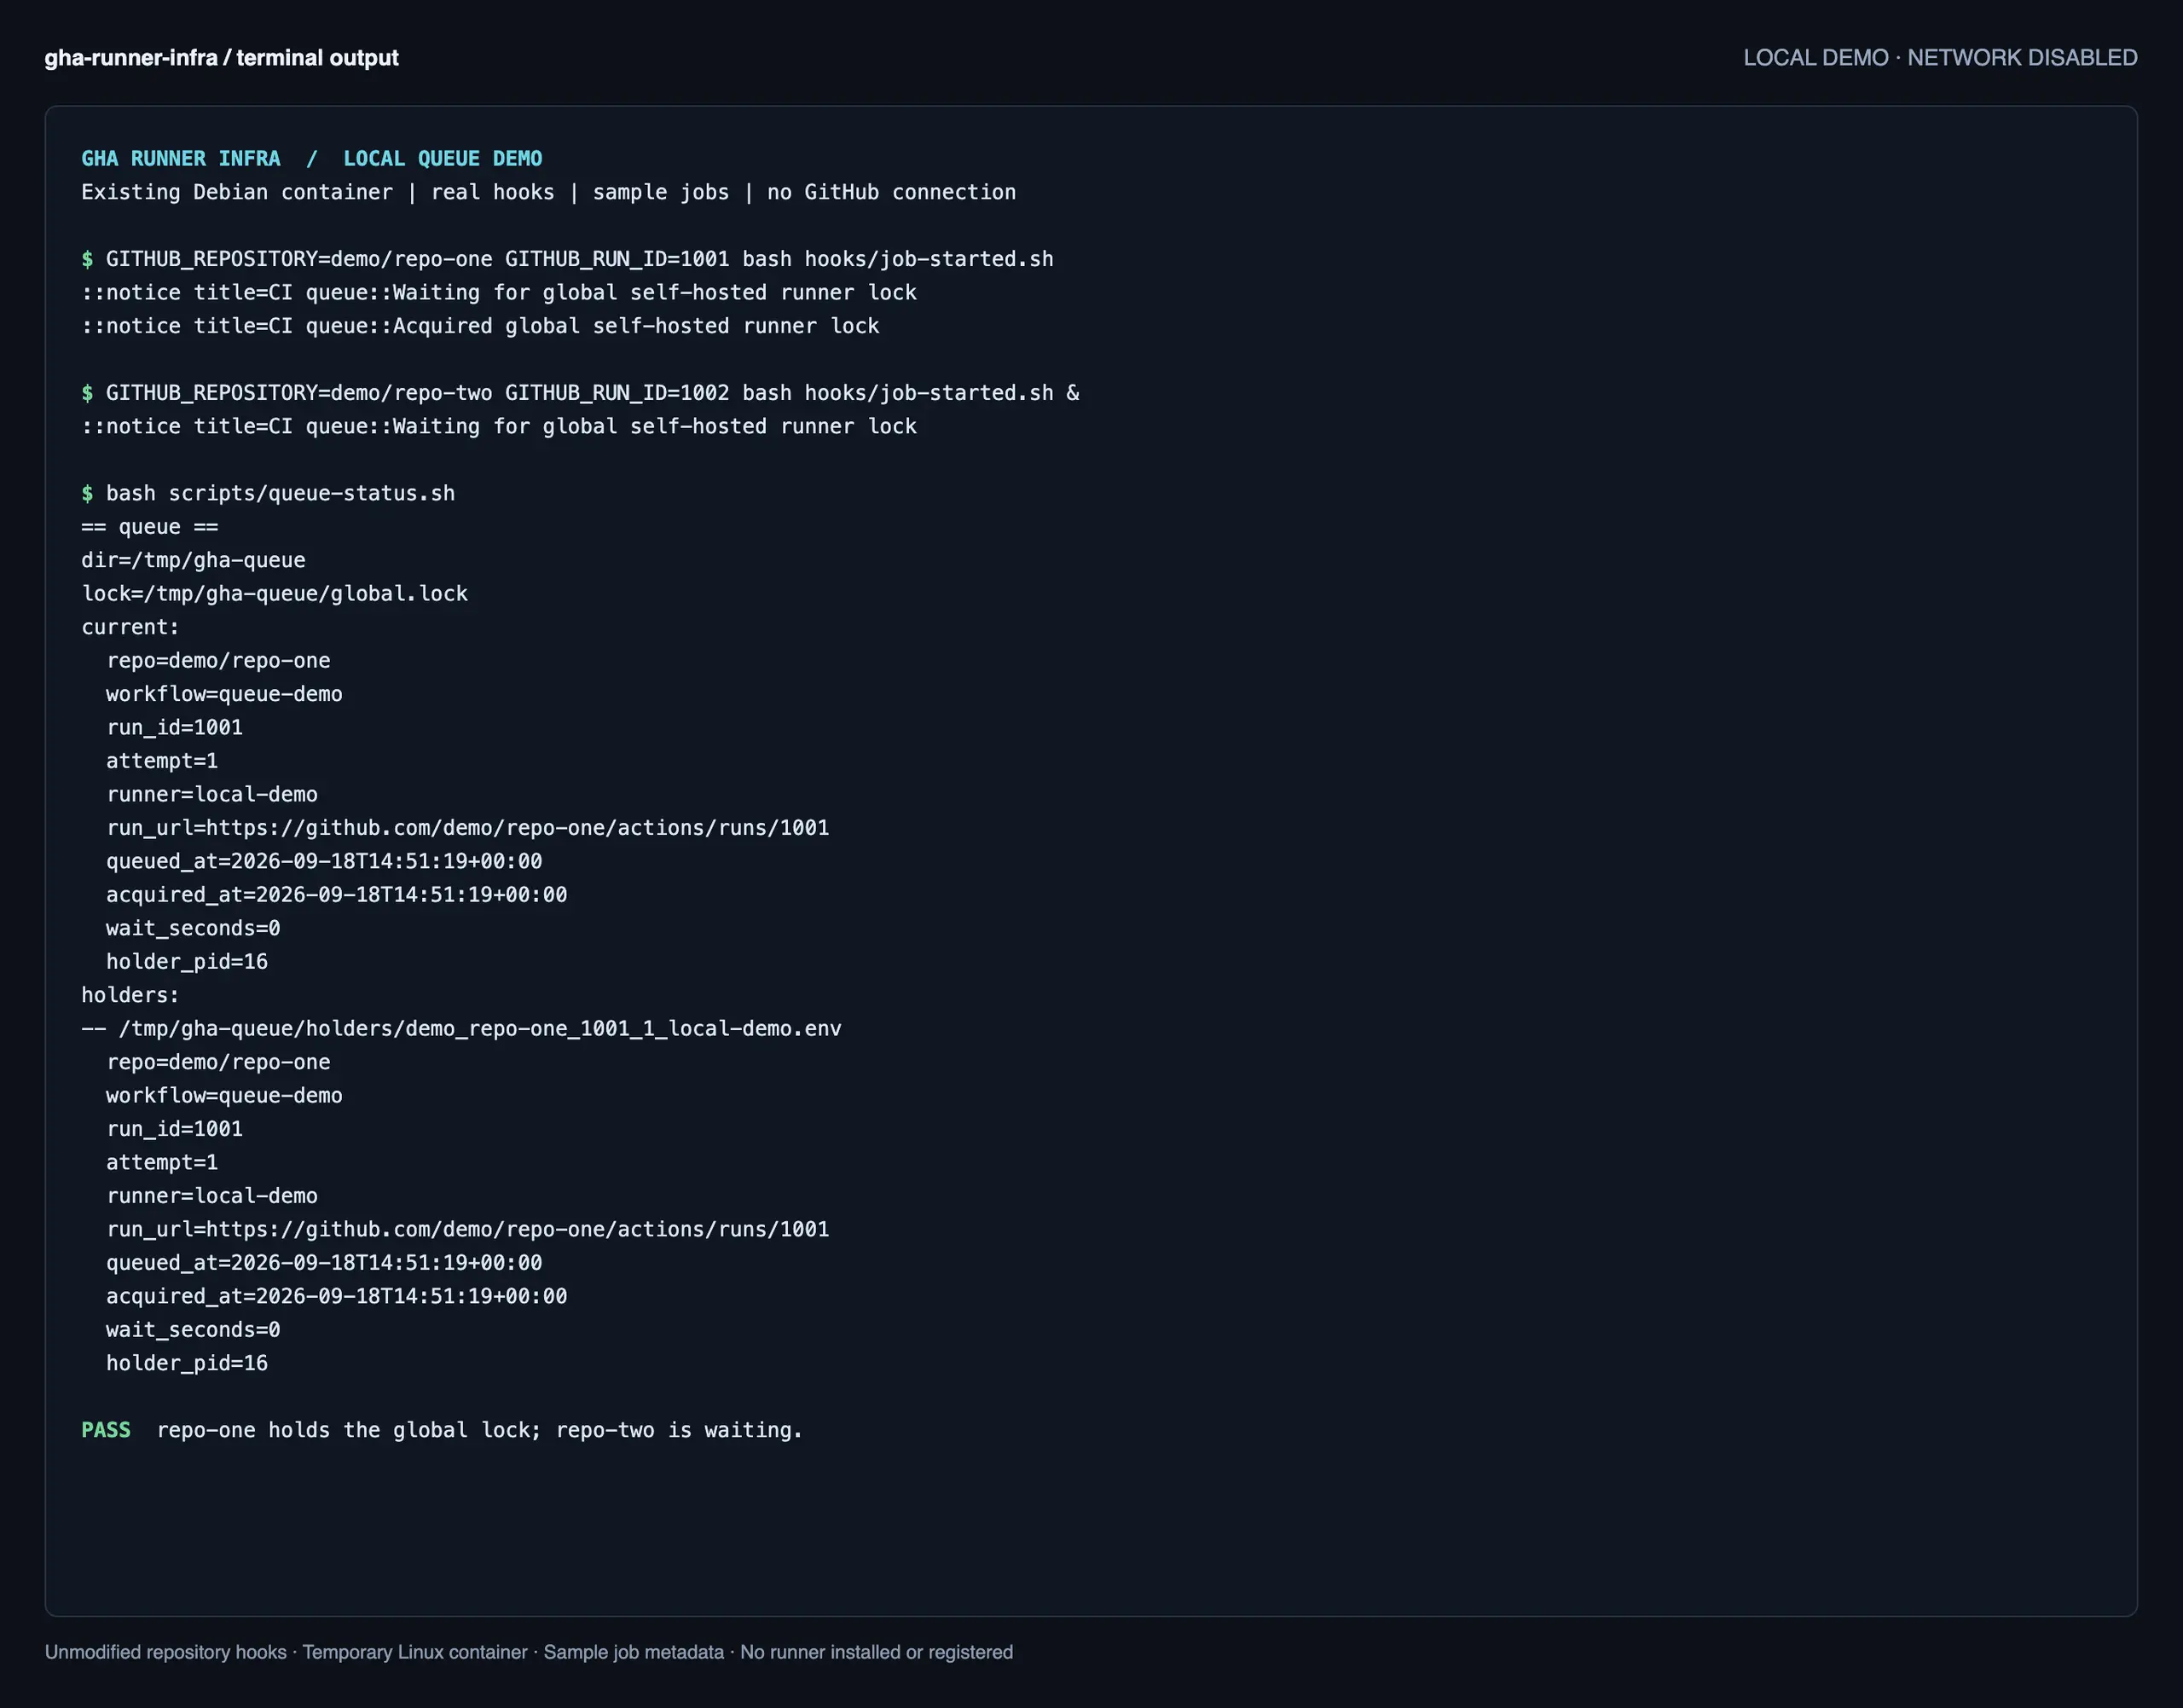
Private setup for GitHub Actions runners
GitHub Actions Version 0.1.2
GHA is my private setup for running GitHub Actions runners for multiple repositories on one VDS. It handles runner registration, a shared job queue and resource limits, letting me run CI jobs on my own server while keeping the workflows in GitHub.
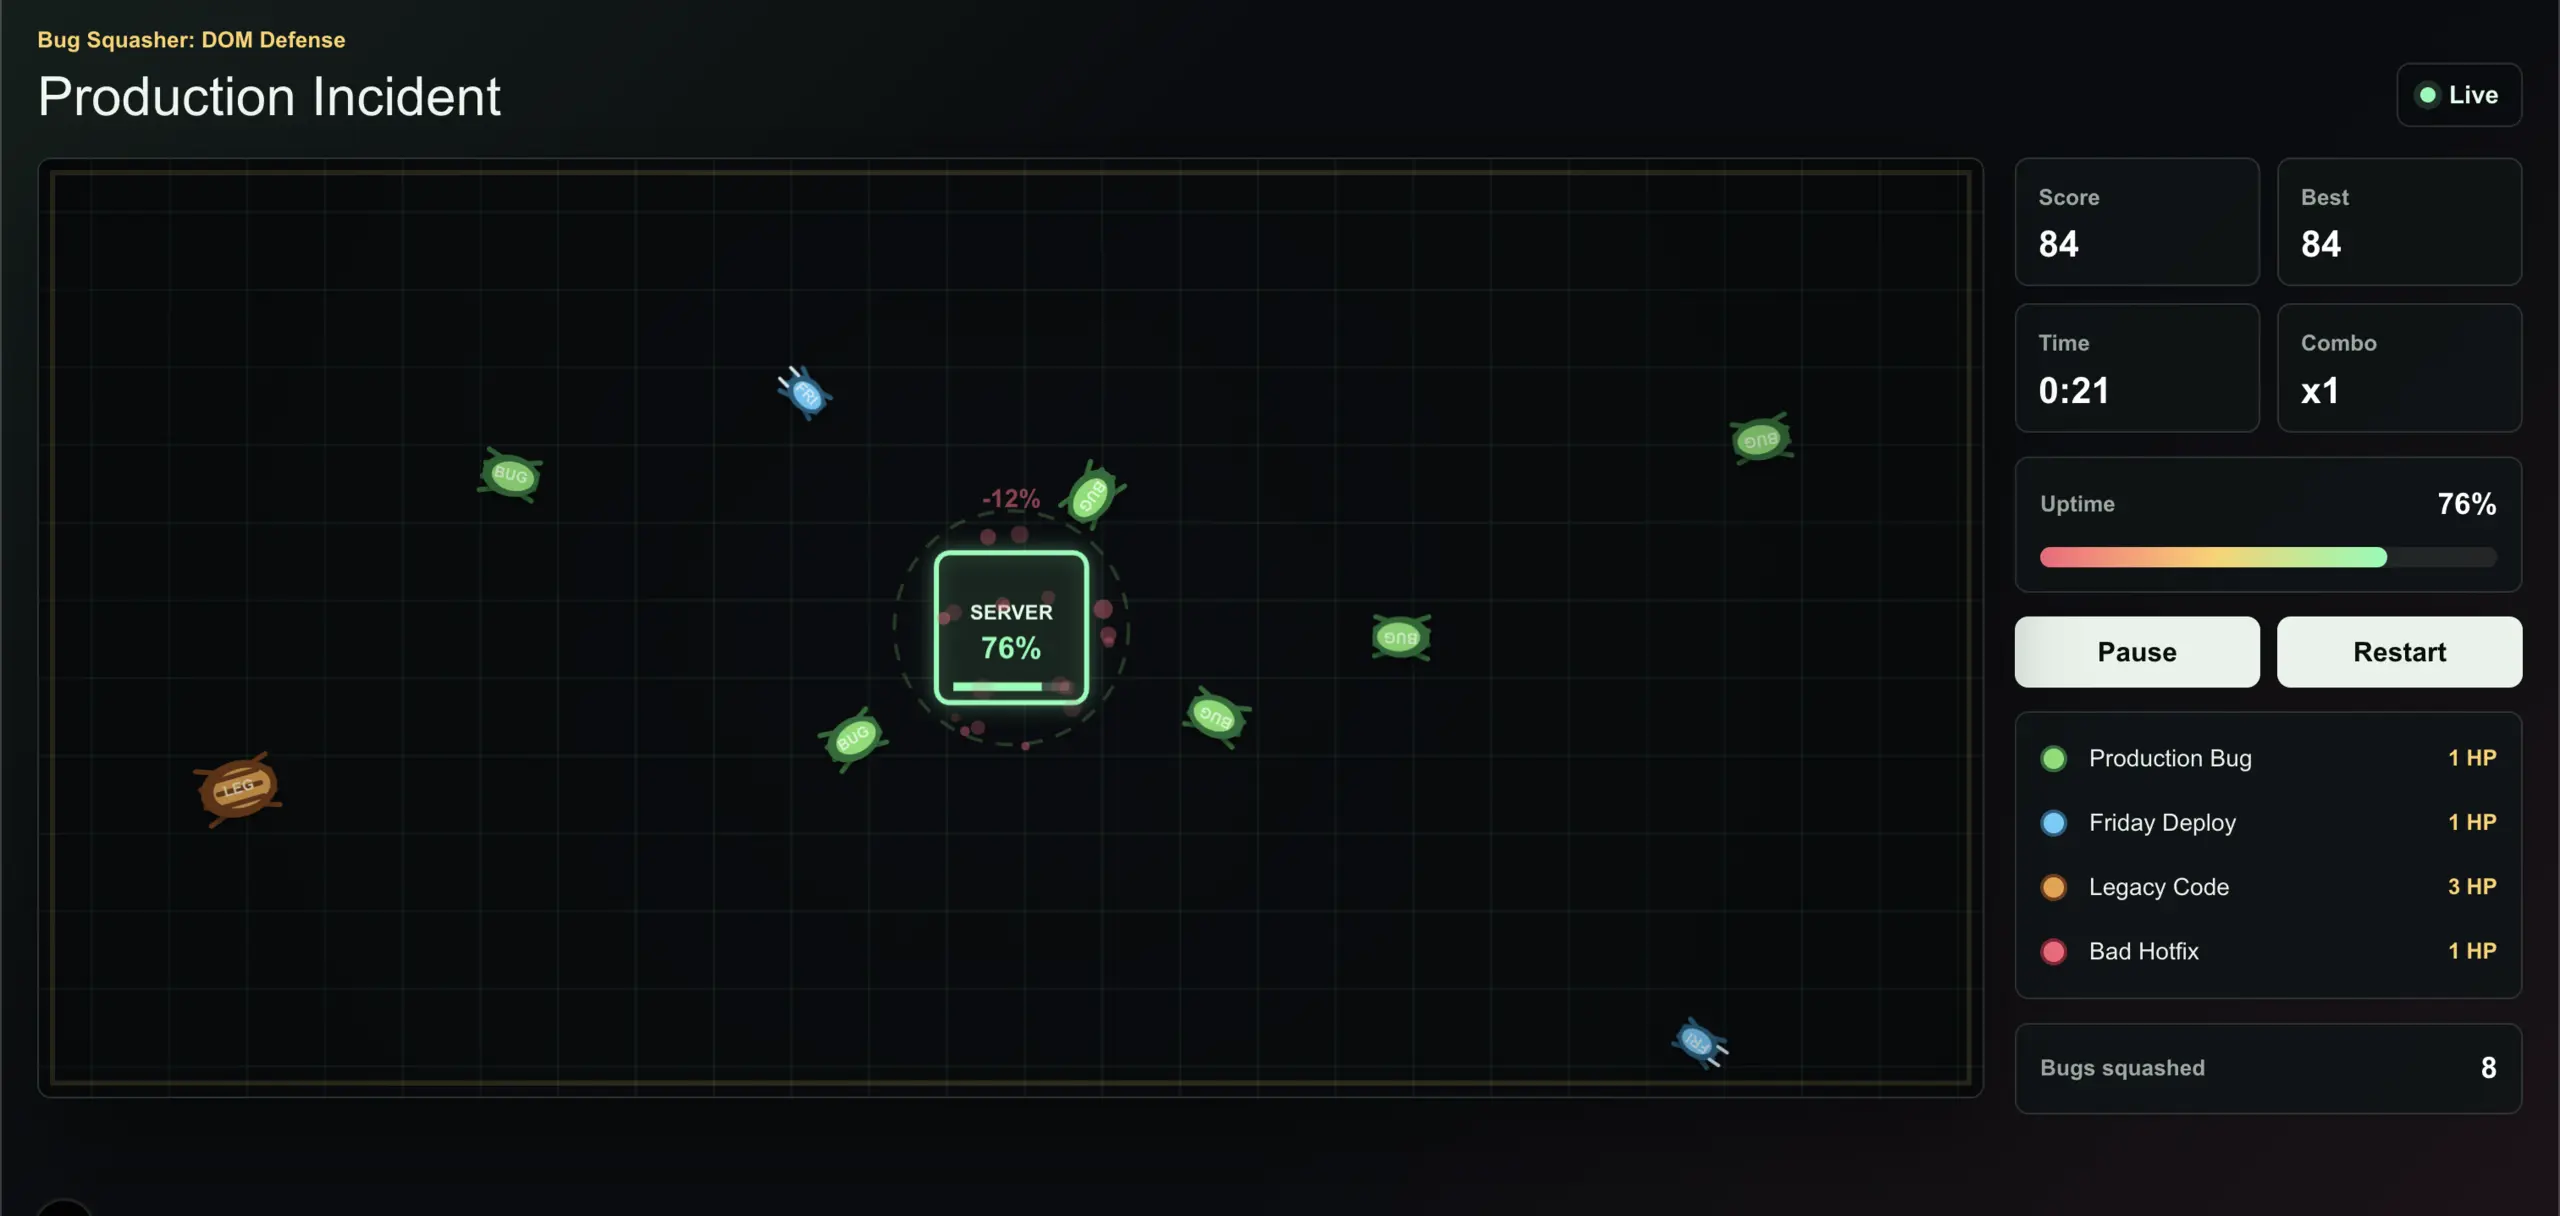
Bug Squasher: DOM Defense
TypeScript Version 0.1.0
I was bored and wanted a break from client projects, so I made a little TypeScript game. Naturally, it ended up being about bugs taking down a server.
DG6 — Multilingual pSEO Publishing
PHP Version 1.0.0
A Laravel publishing application for my programmatic SEO projects. DG6 turns generated content into multilingual websites, with separate domains, themes and publishing schedules, all running from one codebase.
DG6 Swarm — AI Content & Media Pipeline
Python Version 0.17
A Python pipeline that turns a domain and starting keyword into site copy, articles and visual assets. Specialized GPU workers handle each stage, starting and stopping according to queued work.